


One Kingdom. Many Regulators. One View.
A bank in Riyadh answers to SAMA, the National Cybersecurity Authority and SDAIA. A listed company adds the Capital Market Authority. An energy group adds NCA controls for its operational technology and oversight of a large contractor network.
As Vision 2030 accelerates, each regulator publishes its own controls, templates and reporting cycle, and the NCA now has penalty powers over private-sector entities. Most teams still reconcile it all in spreadsheets. Keep your advisors; give them one platform to work from.
LockThreat maps your obligations once, tests your controls continuously, and gives your board one current view of risk across the Kingdom.
The Bar Has Been Raised.


Built for the Kingdom’s Most Regulated Sectors
NCA ECC-2:2024, CSCC and cloud controls, with on-premises options.

SAMA cyber, IT governance, BCM and counter-fraud frameworks.

CMA cybersecurity guidelines and corporate governance rules.

PDPL sensitive-data duties for hospitals, labs and health-tech.

NCA OT controls and contractor risk at scale.

NCA’s new private-sector controls and PDPL, group-wide.
Spreadsheets and IT-Only Tools Leave agapRegulators Will Find.
GRC


Frameworks for Saudi Arabia
Mapped to one control library, so a control tested once serves every framework it supports. Tracking something not listed? Ask us.


National Cybersecurity (NCA & CST)
Data Protection & Data Governance
Banking & Fintech (SAMA)
Capital Markets & Governance
Global Standards


Your teams are already using AI on customer and citizen data. Under the PDPL, you’re accountable for it. Do you know which AI tools and agents are breaching your controls?


Your Data. In the Kingdom.
Saudi rules keep sensitive data close to home: the Cloud First Policy keeps government cloud data inside the Kingdom, and PDPL transfer rules set a high bar for sending personal data abroad.
Choose how LockThreat runs: managed SaaS hosted in the Kingdom, your own private cloud, or on-premises in your data centre. The same full G+R+C depth, regardless of deployment.


One Platform for the Whole Buying Committee


- One evidence trail for NCA assessments, SAMA reviews and CMA requirements.
- Third-party and contractor risk tracked alongside your own controls.

- Risk quantified in financial terms with FAIR modelling and Monte Carlo simulation.
- Policies and gap analysis generated against the frameworks you answer to.

- PDPL, transfer rules and DPO duties mapped to controls, with the 72-hour breach clock tracked.
- Visibility of AI tools handling personal data.

- Continuous control testing instead of periodic sampling.
- Board and committee reporting drawn from live data, not spreadsheets.

Everything Enterprise GRC Should Have Been.
Most GRC tools deliver compliance, with governance and risk as an afterthought.
Here, governance comes first: the policies that move your organisation forward, the controls that contain risk across every department, and the compliance that follows naturally from both.
No spreadsheets. No disconnected tools. No point-in-time snapshots. One centralised, ongoing view of your risk and compliance posture.
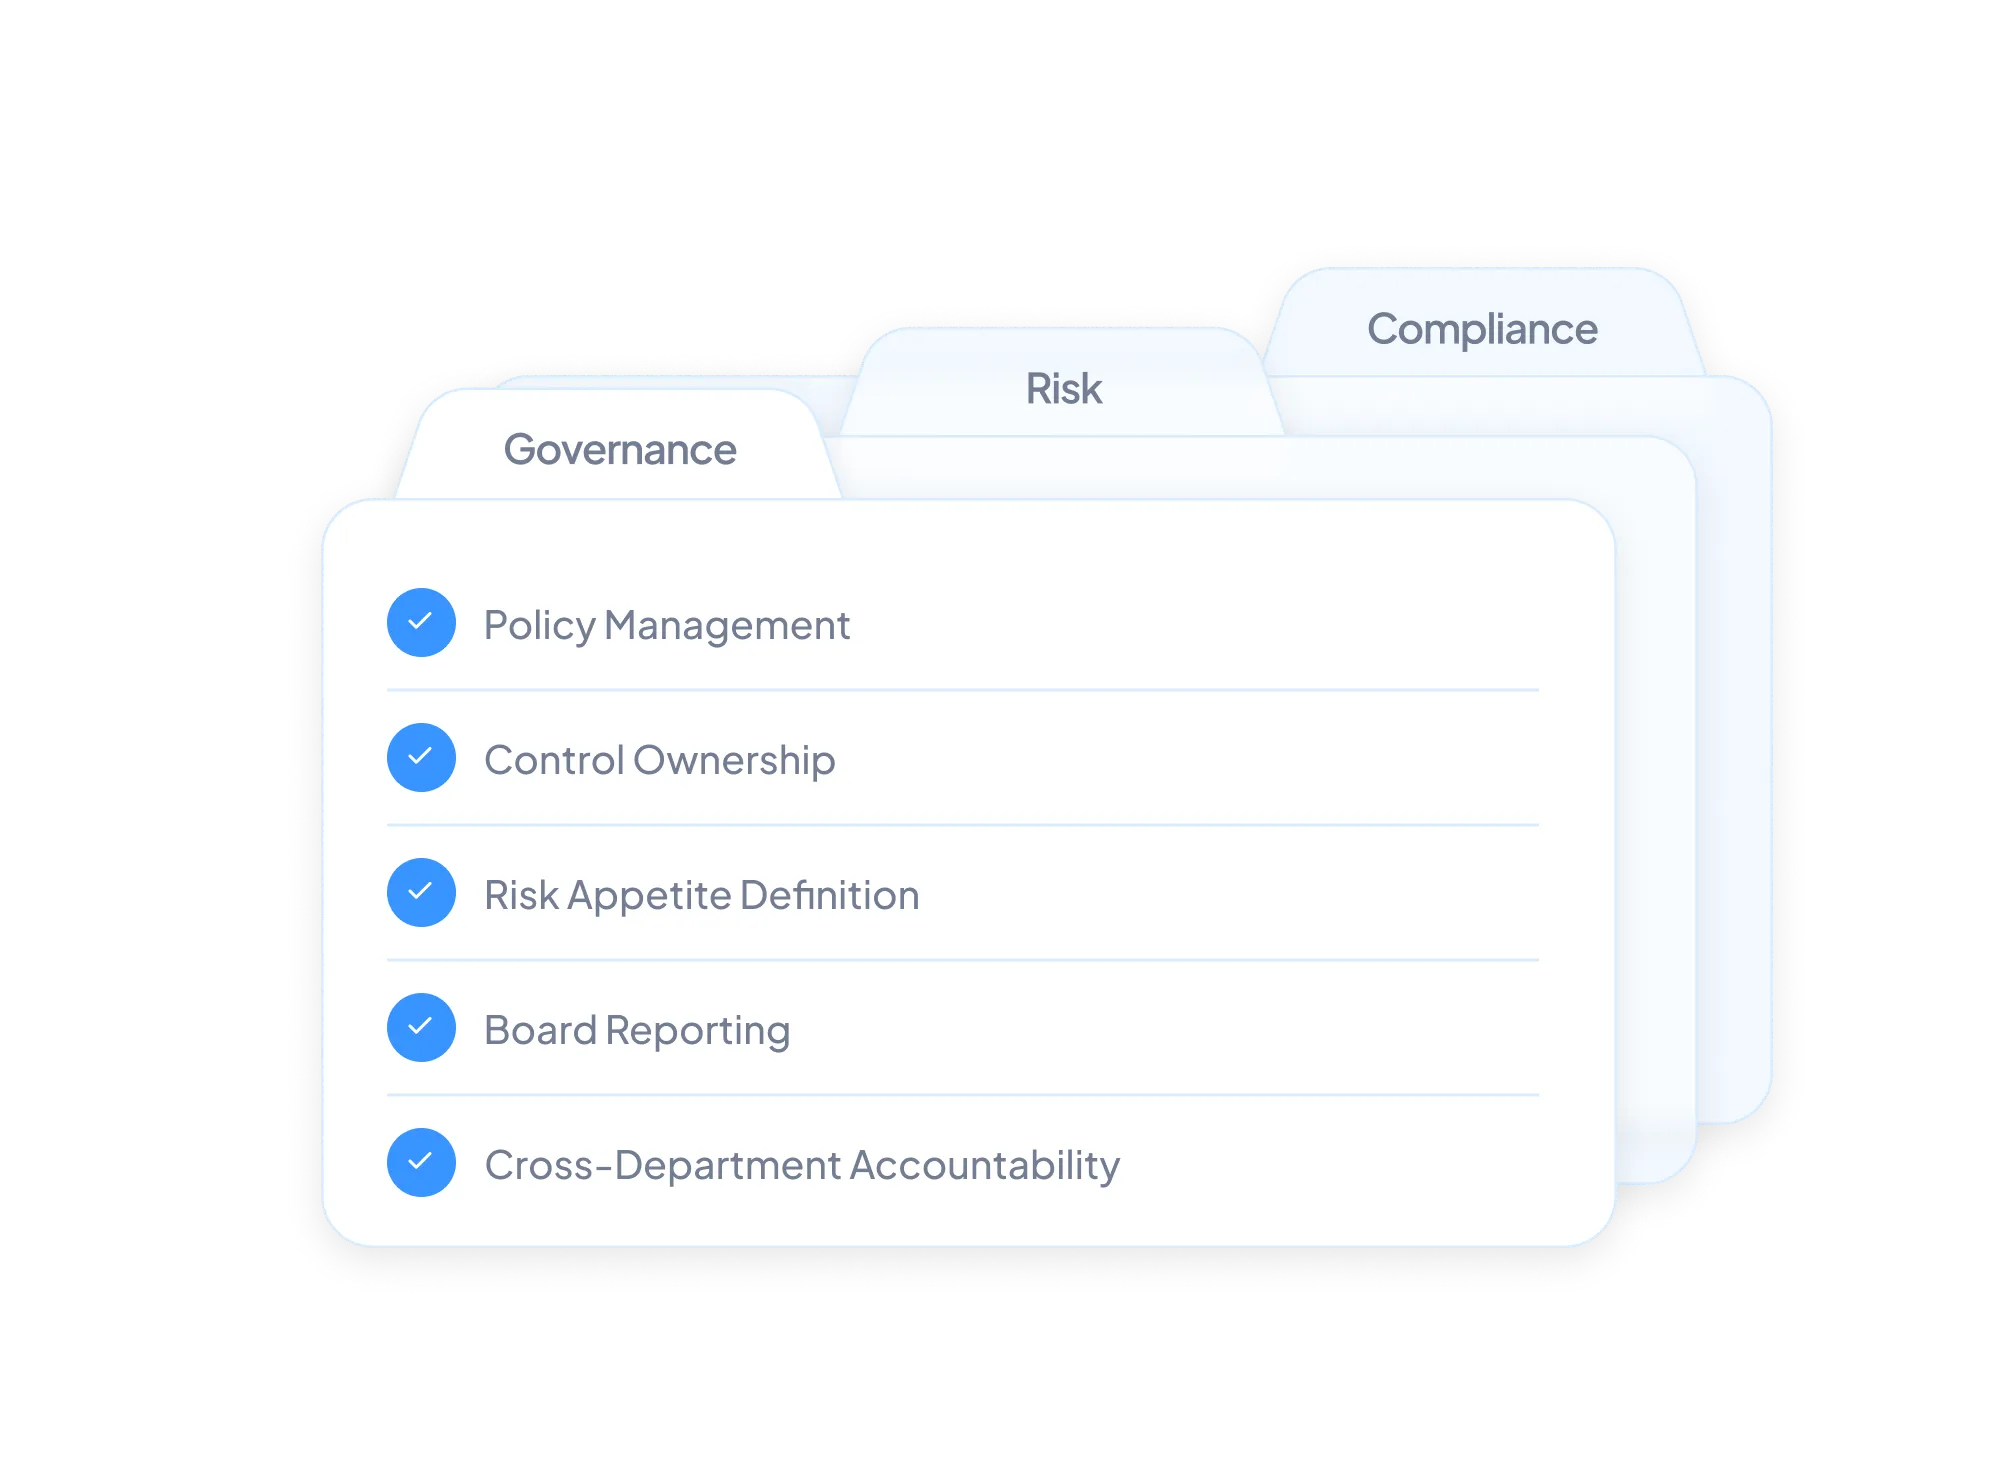

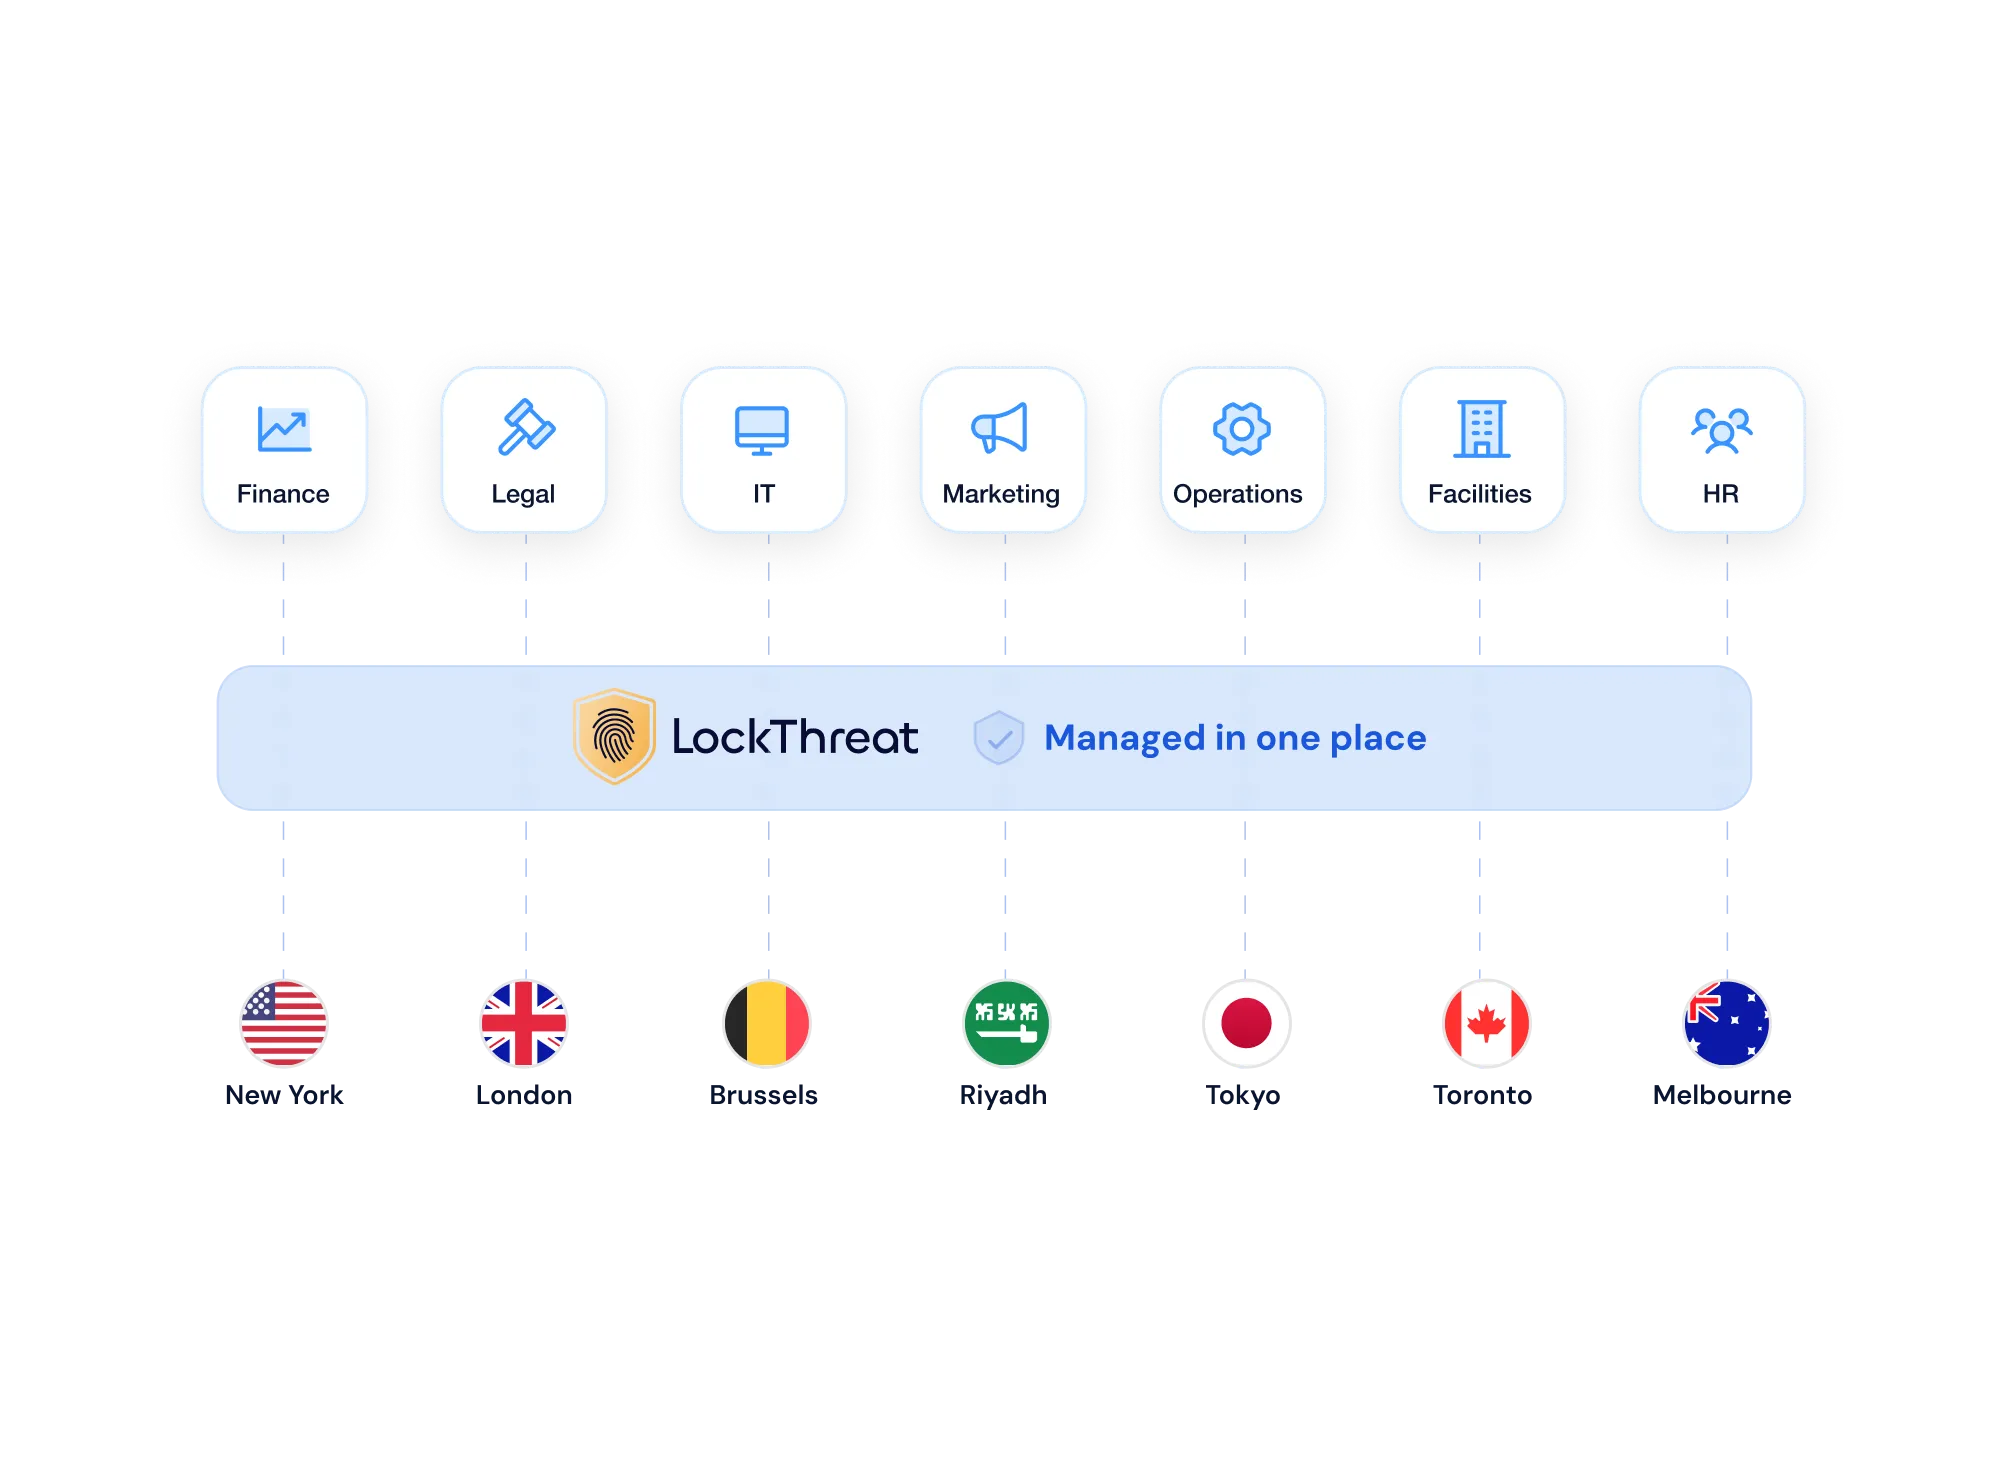
Your regulatory obligations don’t respect org charts or borders.
Every department, from finance, legal and HR to operations, cyber and IT, managed in one place, without the sprawl.
The sites you operate in, from Riyadh, Jeddah and Dammam to NEOM and your offices across the GCC, managed in one place without adding more tools.

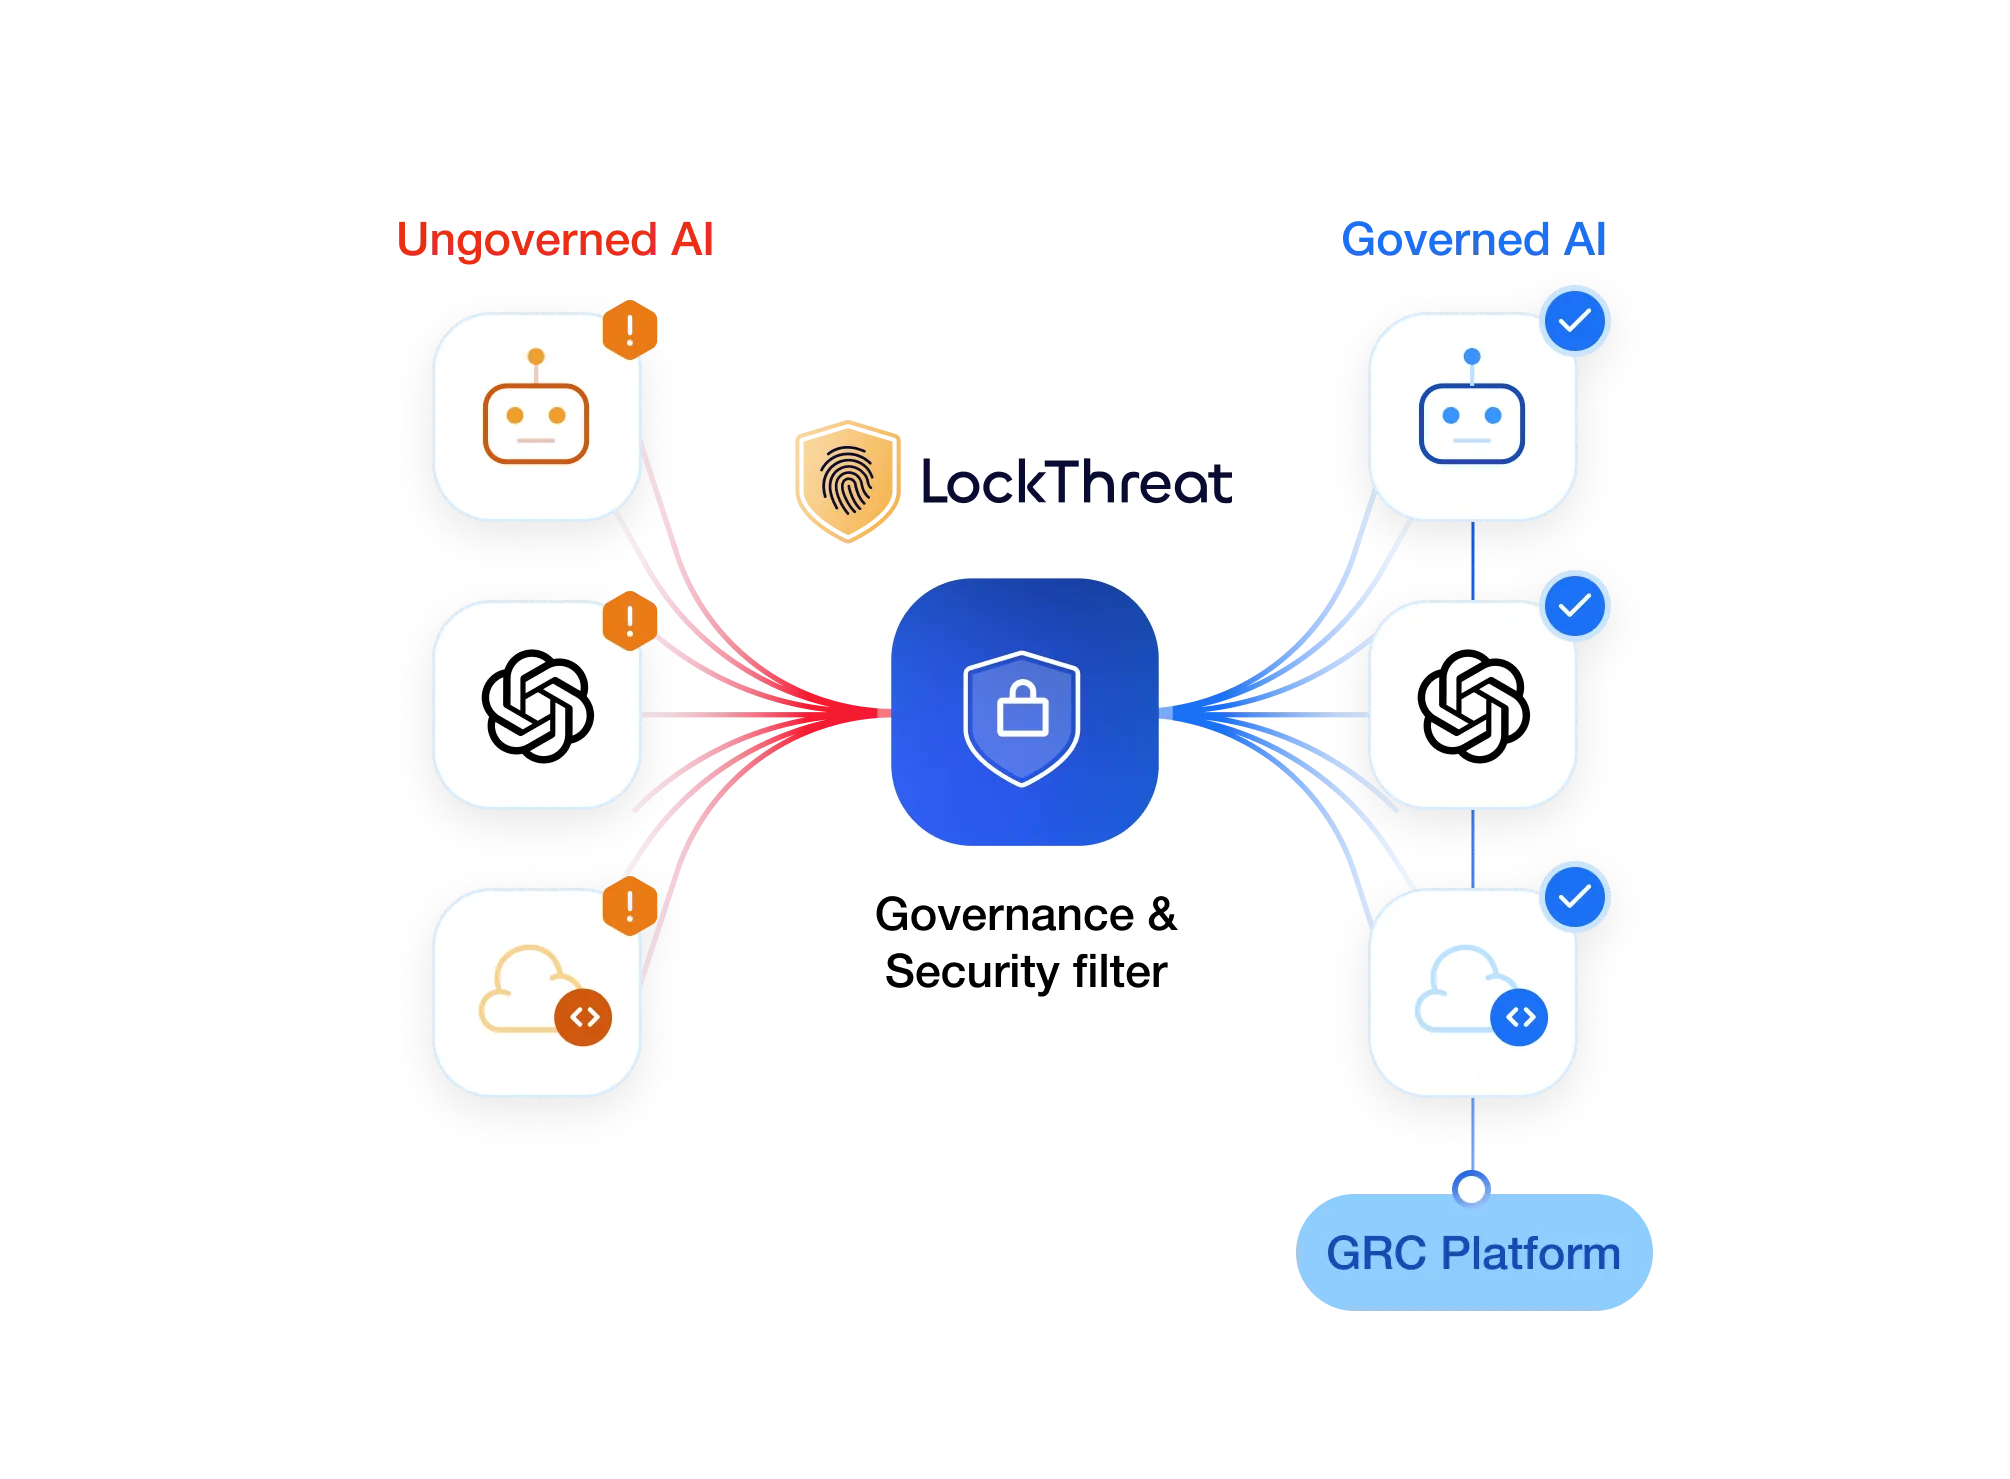
Which AI tools are your employees using? Are they approved? Are they handling personal data they shouldn’t under the PDPL?
And when AI agents act autonomously, accessing systems, making decisions, breaching controls, who’s watching? Now you are.
From shadow AI discovery and ISO/IEC 42001 alignment to real-time prompt protection and agentic control enforcement, reported directly into your GRC framework.

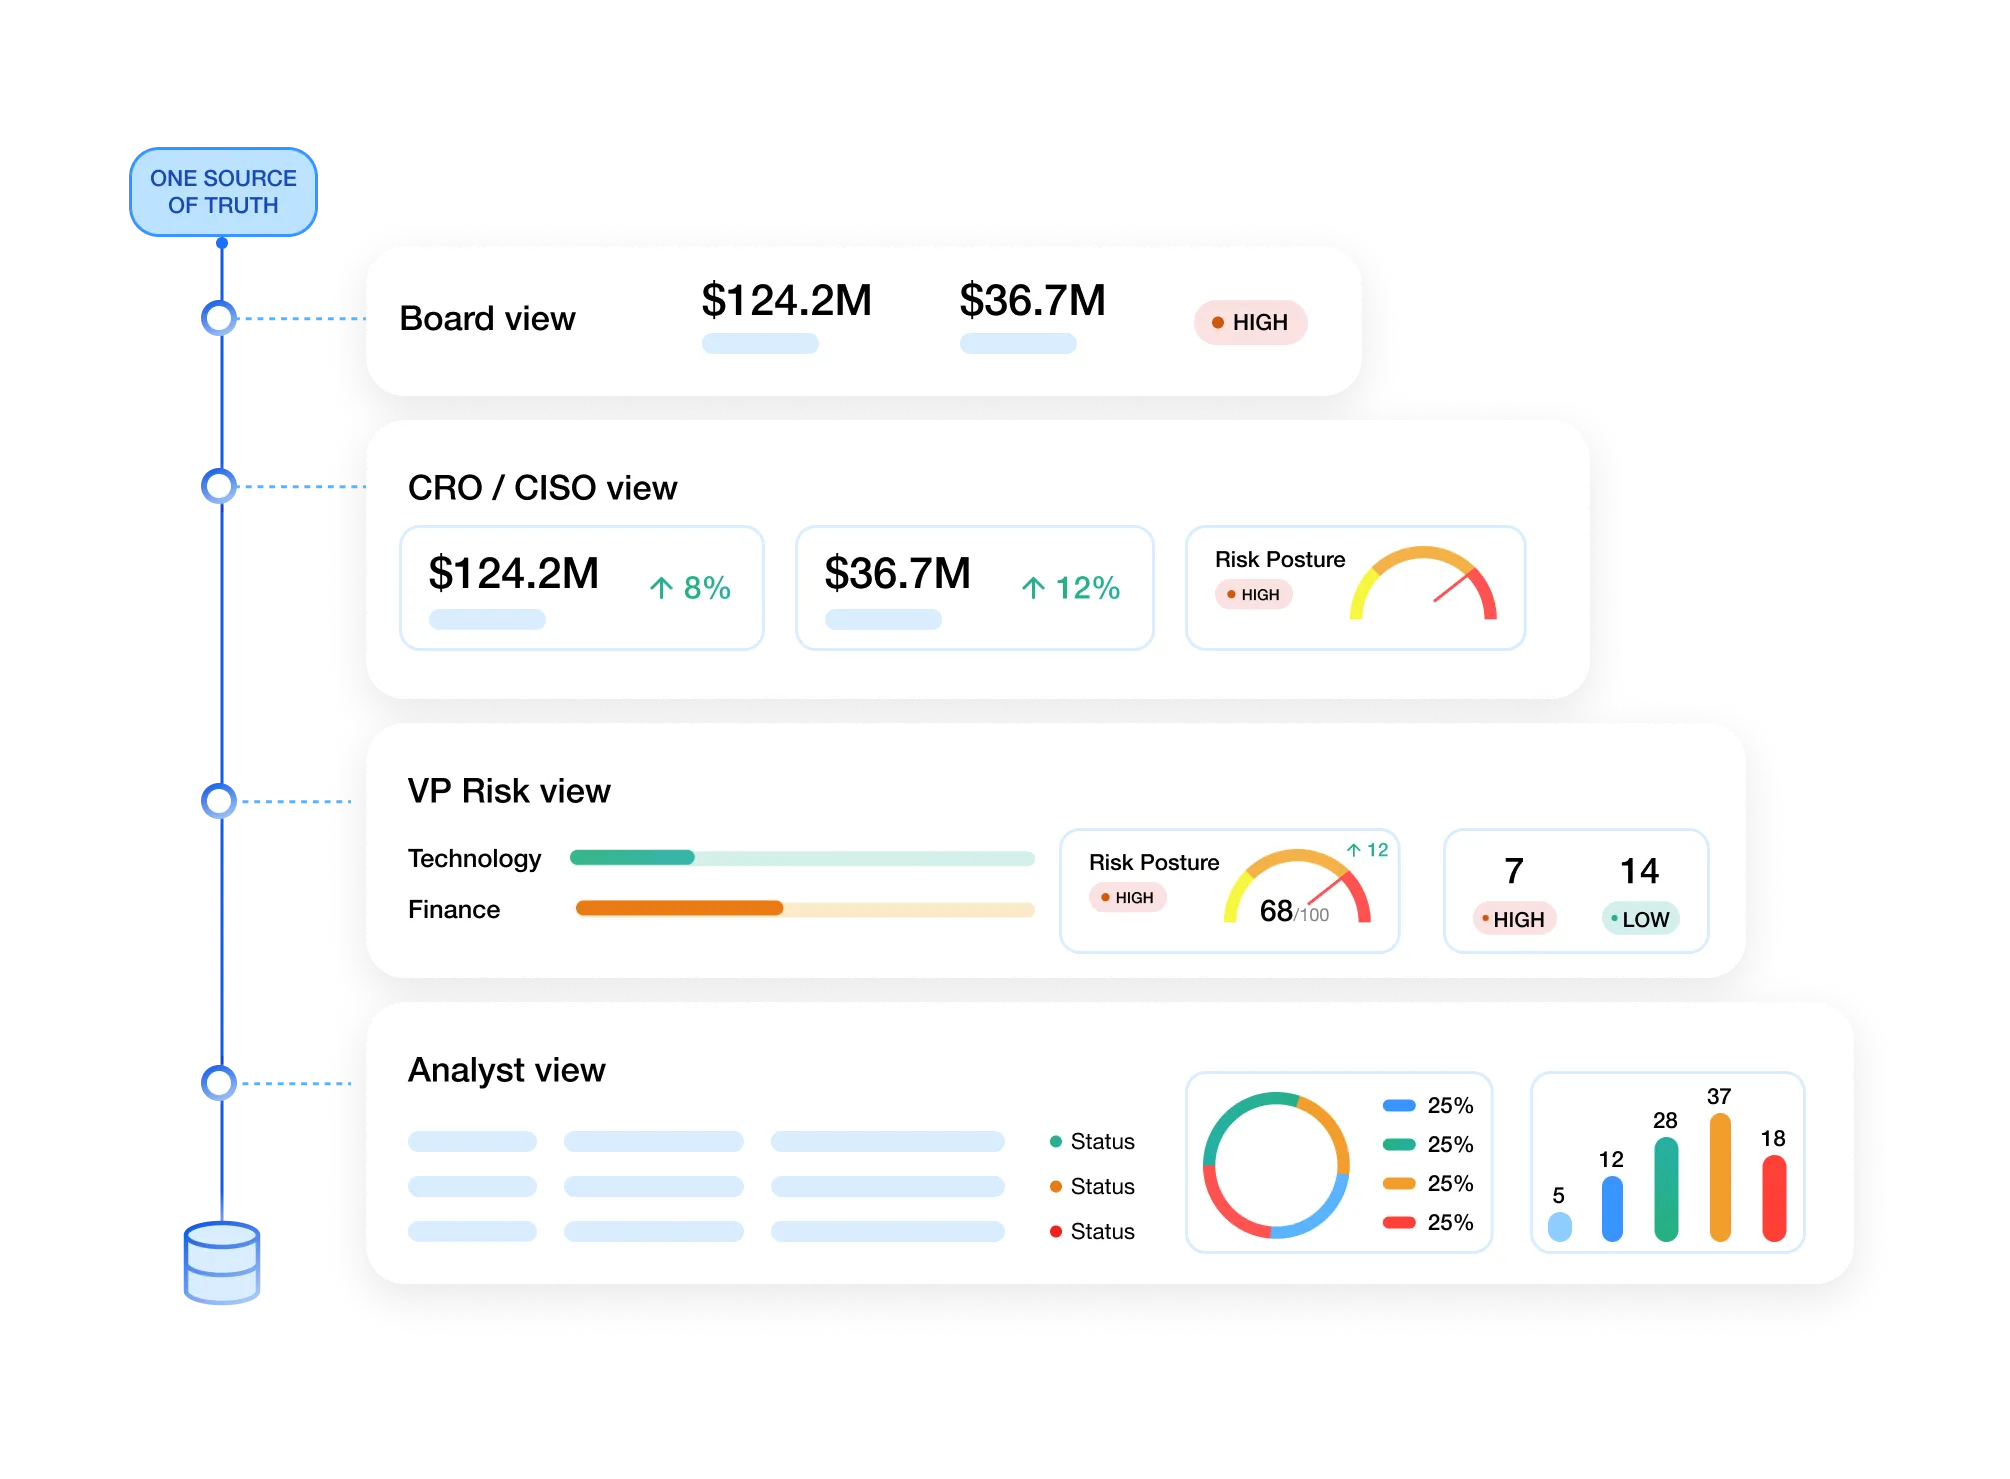
Every stakeholder needs a different view of the same risk reality, from one source of truth.
Express risk in financial terms your board and CFO can act on, using FAIR modelling and Monte Carlo simulation.
Detailed enough for the analyst, clear enough for the Chief Risk Officer and the CISO, compelling enough for the board.

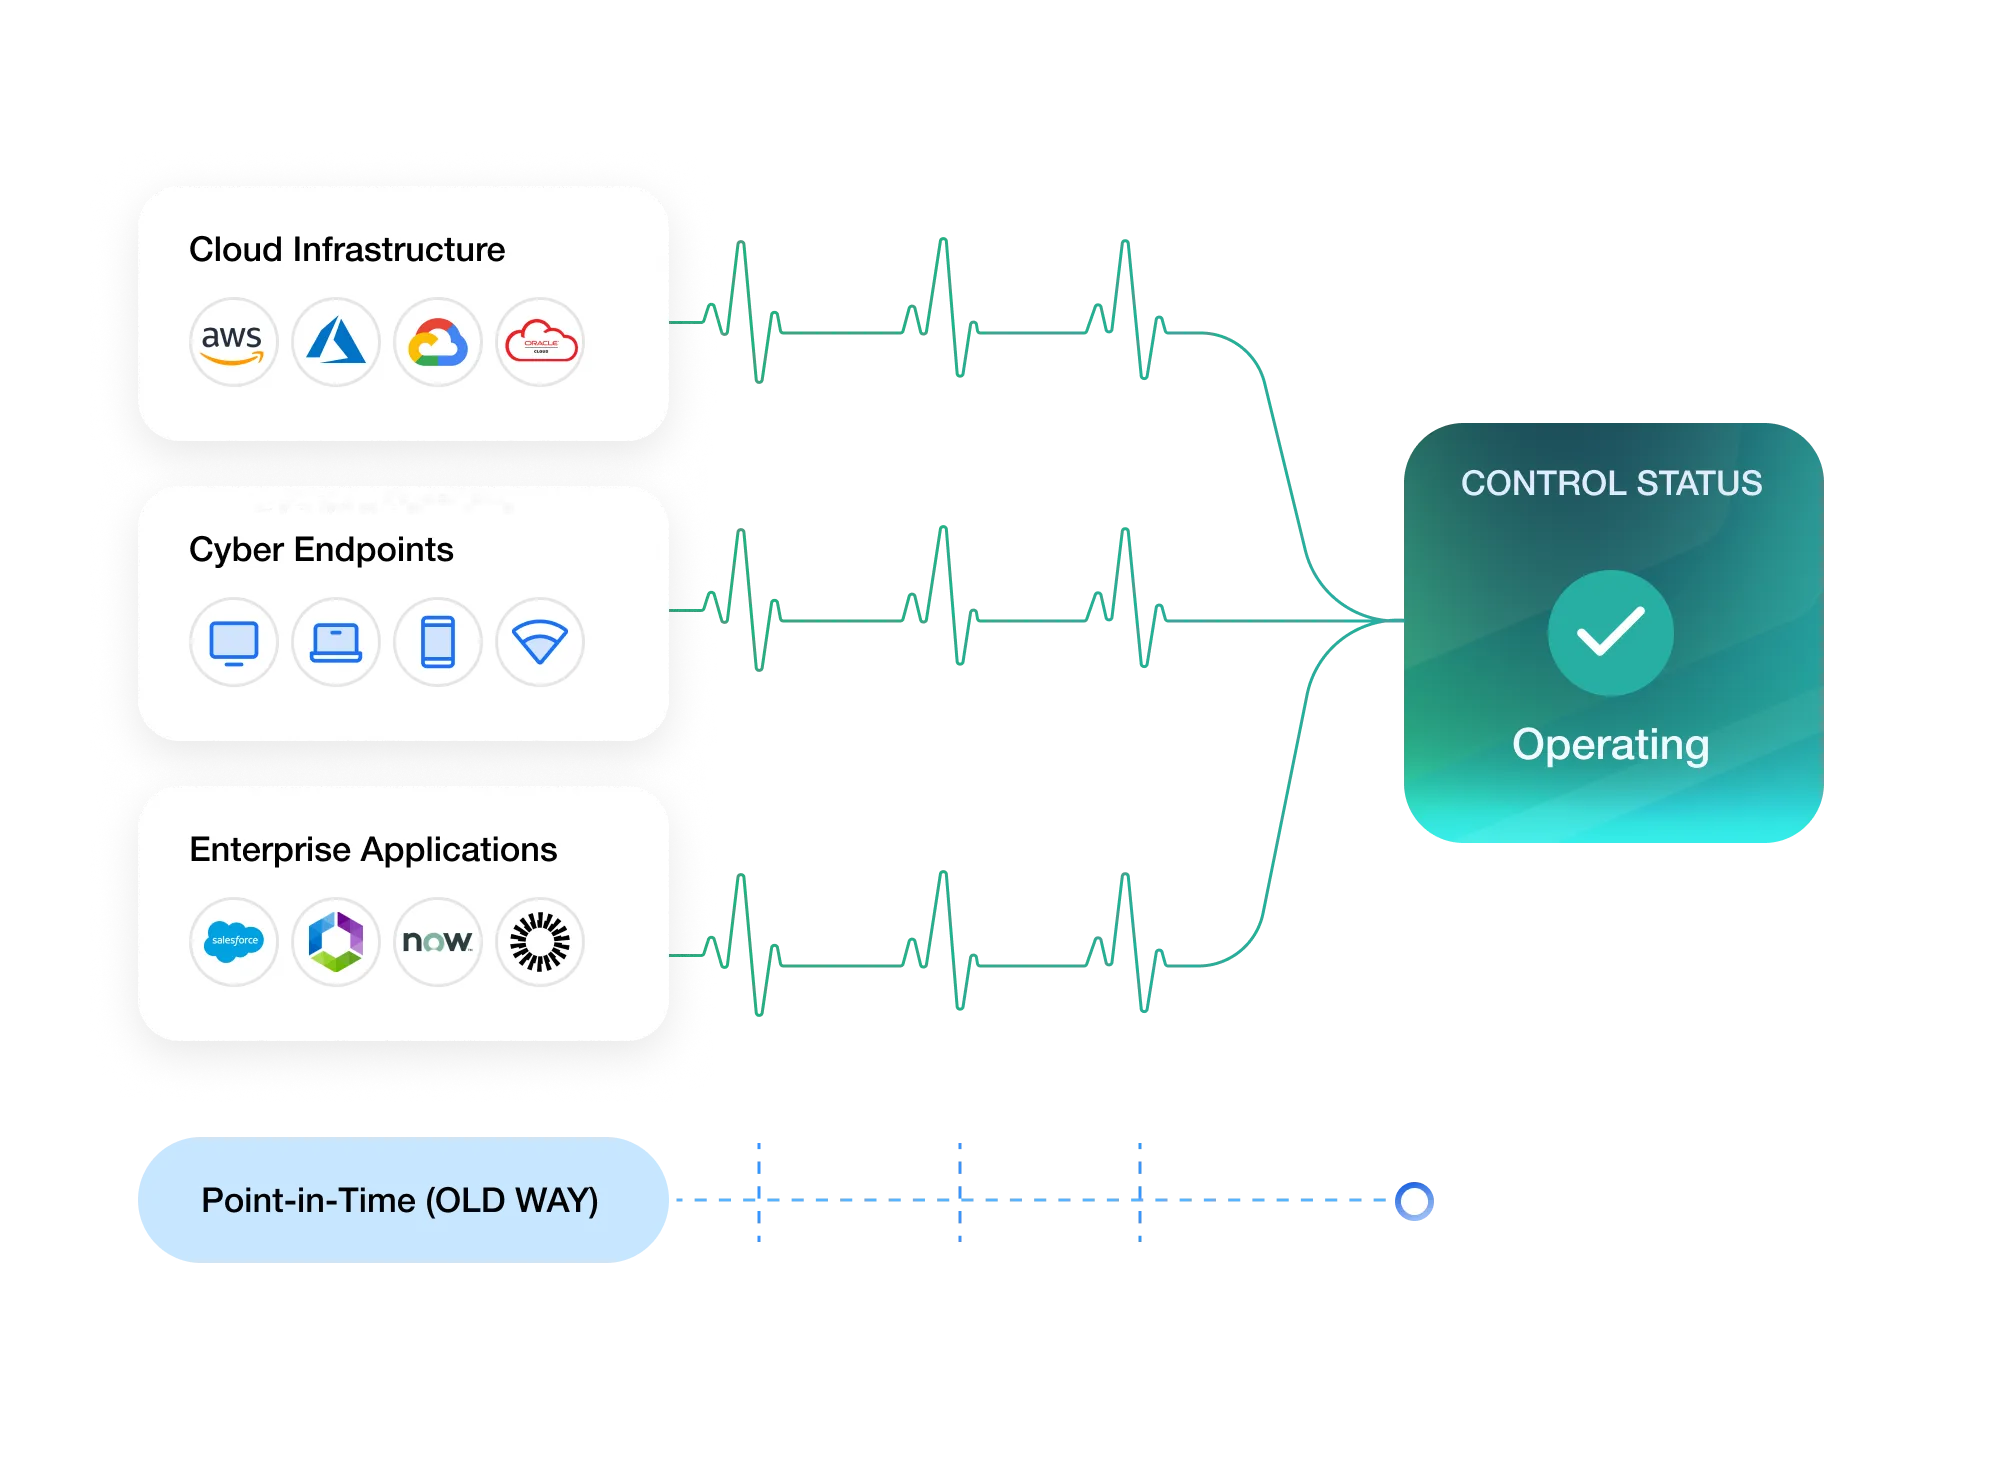
Compliance isn’t an annual exercise; it’s an ongoing operating requirement.
LockThreat validates that your controls are working, right now, across cloud infrastructure, cyber endpoints and enterprise applications.
Far less scrambling for evidence before an NCA assessment, a SAMA review or a CMA inspection.

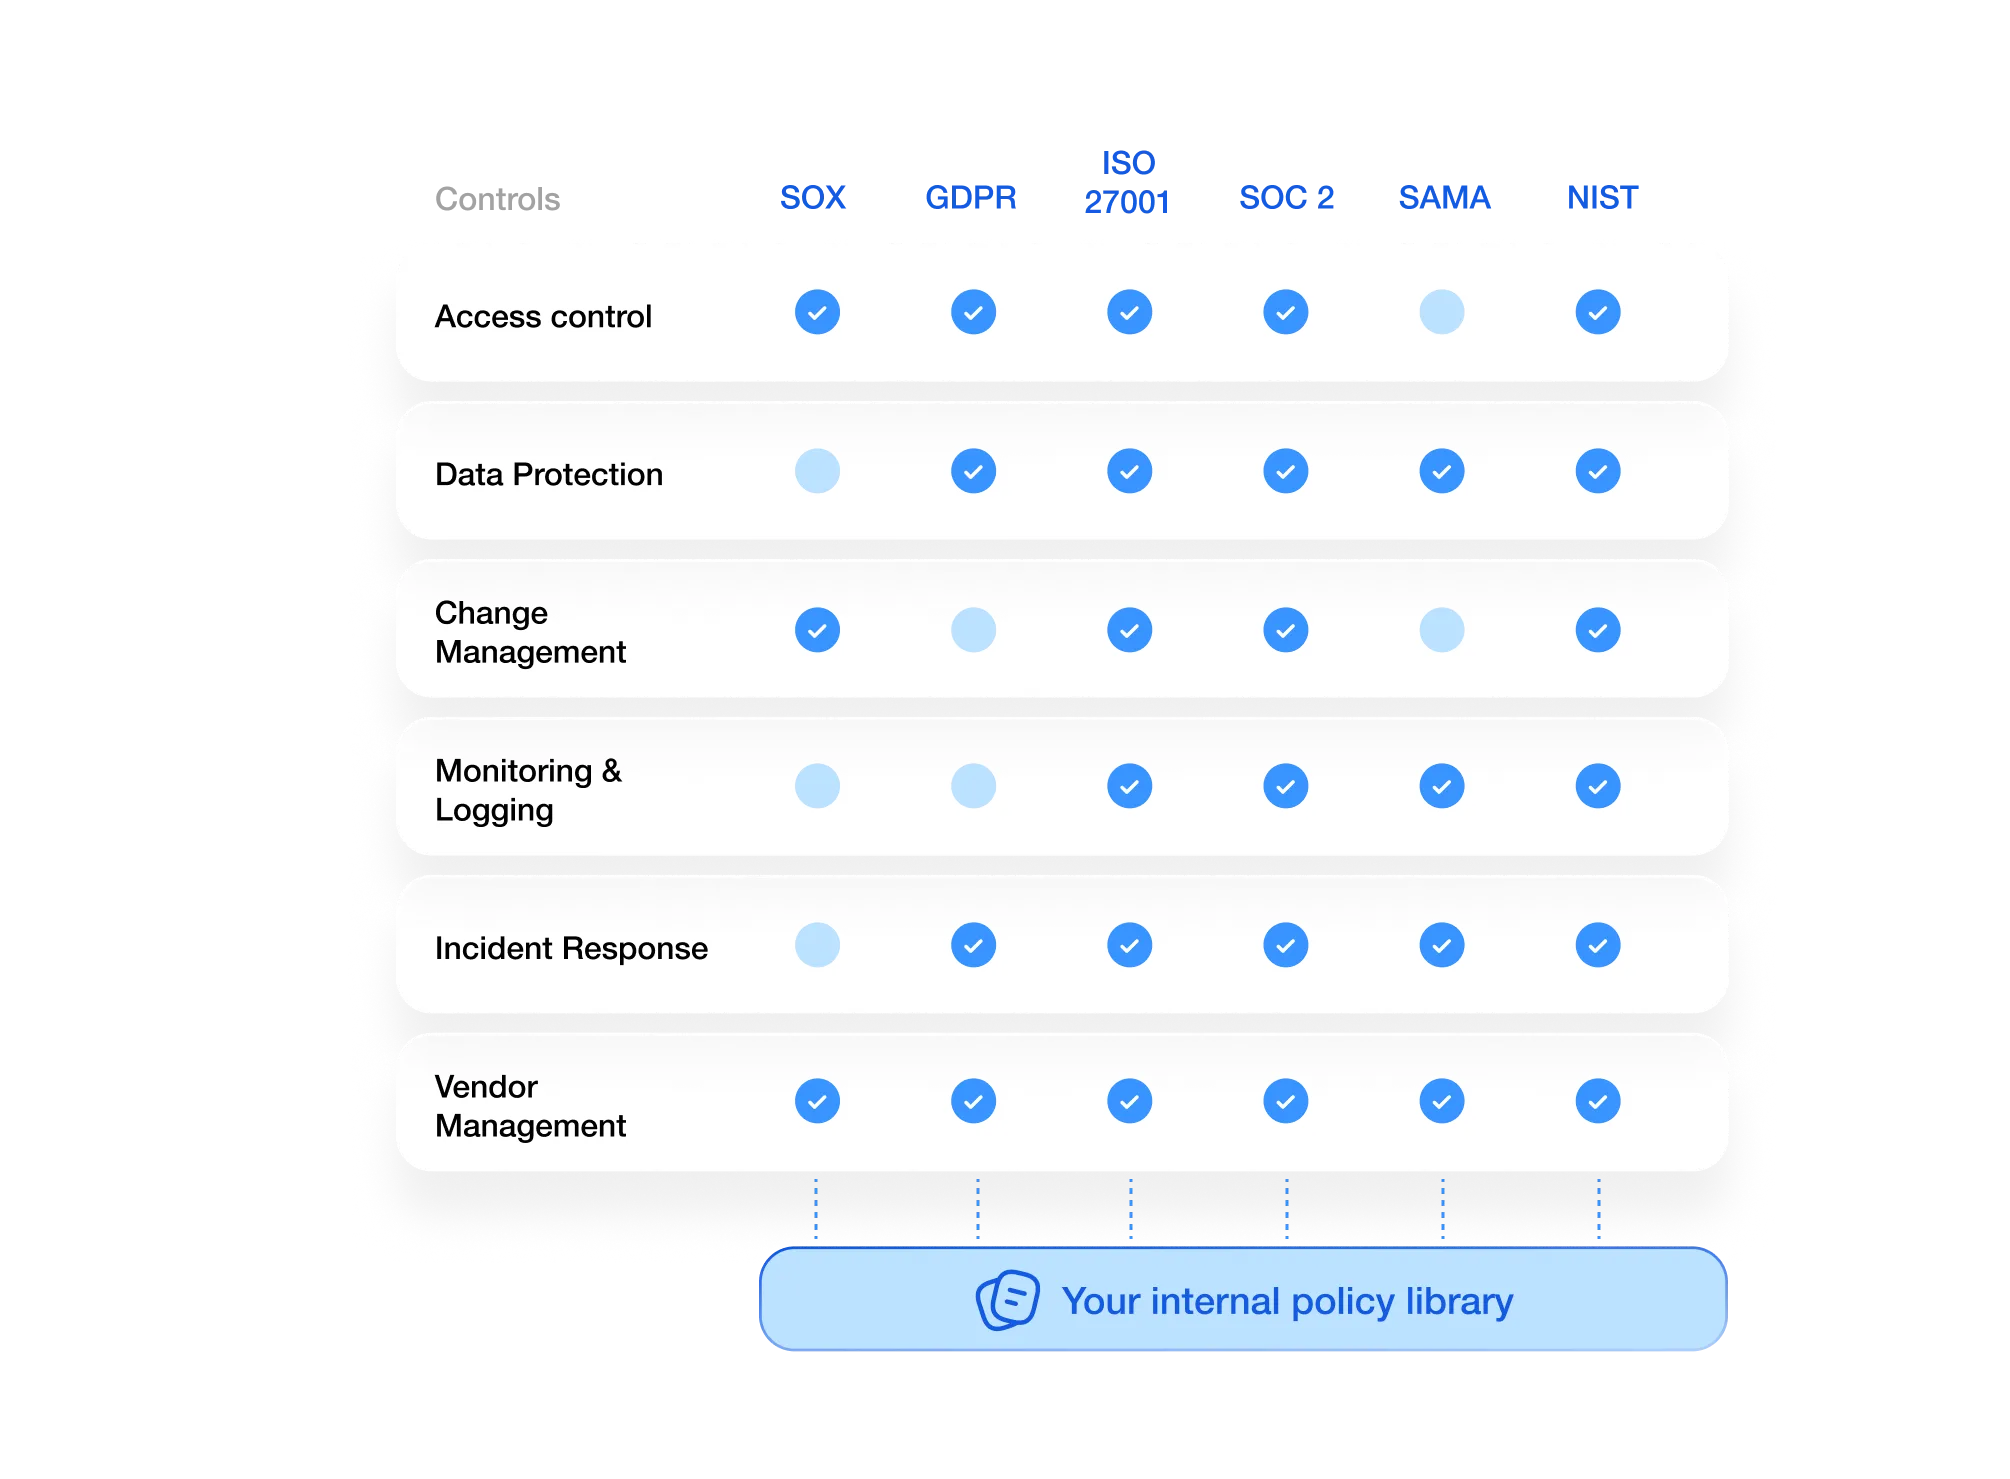
Map NCA ECC-2, SAMA CSF, PDPL and the CMA guidelines to ISO 27001, NIST and SOC 2, and to each other, eliminating redundant work.
Tie everything to your own policy library and control framework, so governance becomes a living system, not a compliance filing cabinet.

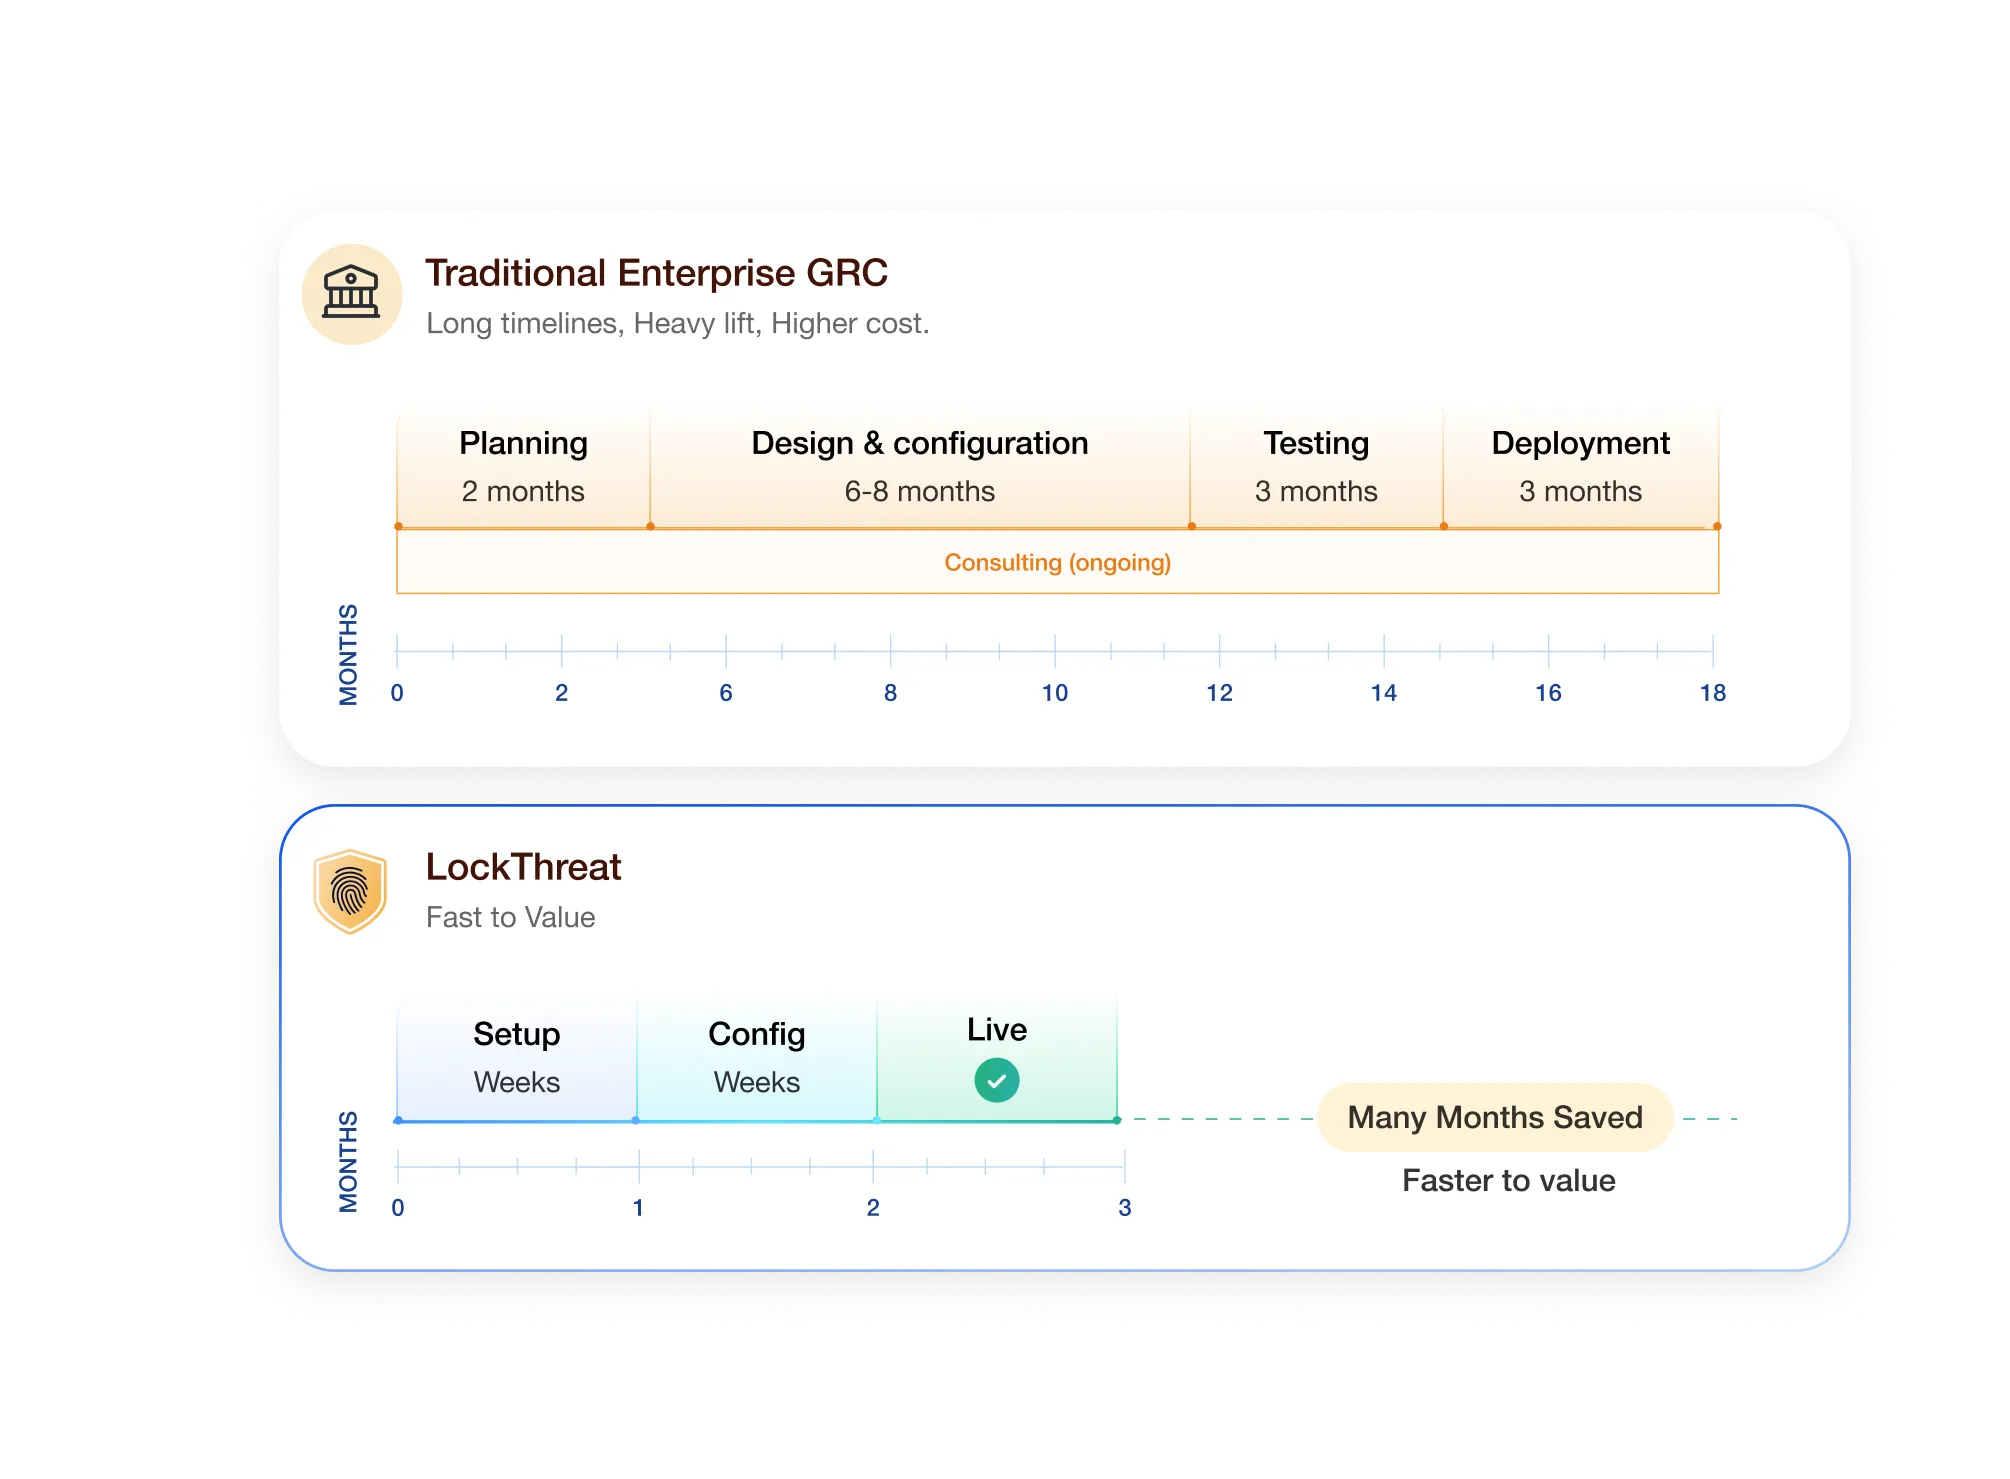
Enterprise GRC depth without the 18-month implementation. Up and running in weeks to months, on the technology stack you already have.
Implemented and supported by our in-region team and partners.
Already running another GRC platform? Run LockThreat alongside it during transition, no rip-and-replace required.


What GRC Leaders Say


See LockThreat on Your Saudi Frameworks
A focused 30-minute walkthrough, plus pricing for your deployment. No generic pitch, no obligation.
Tell us which regulators and frameworks you answer to (NCA, SAMA, PDPL, CMA or CST) and how you need to deploy. We’ll tailor the session to your programme.
- A 30-minute walkthrough on your frameworks, following your priorities.
- Your deployment path: SaaS hosted in the Kingdom, private cloud or on-premises.
- Pricing for your scope, based on your entities, frameworks and deployment model.
Delivered by our in-region team and partners. Prefer email? info@lockthreat.com


