KVKK. BDDK.
SPK. TCMB. One GRC Platform.

Governance, risk and compliance on one control library for banks, payments, capital markets, insurers and energy. Deploy in your private cloud, on-premises or as SaaS.

Already in use with regulated organisations across the Middle East · Live in weeks to months

Every Regulator Has Its Own Rulebook.

A bank in Istanbul answers to BDDK for its information systems, to KVKK for personal data and, since 2025, to the Cybersecurity Presidency for cyber incidents. A broker adds SPK’s new information systems rules. A payment institution adds TCMB’s.

Most teams still stitch this together with spreadsheets, email trails and a tool that only covers IT controls. Governance and enterprise risk stay manual. Keep your advisors; give them one platform to work from.

LockThreat maps your obligations once, tests your controls continuously, and gives your board and Early Risk Detection Committee one current view of risk.

The Stakes Have Risen.

6 Jul 2019
Circular 2019/12
Critical public data, such as health records, kept in Türkiye.
1 Jun 2024
KVKK Transfer Reform
Standard contracts and adequacy replace consent for most transfers abroad.
19 Mar 2025
Cybersecurity Law 7545
Incidents reported without delay to the Cybersecurity Presidency.
30 Jun 2025
New SPK IS Rules
Communiqué VII-128.10 replaces VII-128.9 for capital-market firms.
1 Jan 2026
KVKK Fines Revalued
Maximum data-security fine rises to TRY 17.09 million.

Built for Türkiye’s Most Regulated Sectors

Banks

BDDK IS rules, in-country systems and annual penetration tests.

Payments & E-Money

TCMB information systems rules, updated in September 2026.

Capital Markets & Crypto

SPK VII-128.10, independent IS audits and crypto-asset rules.

Insurers & Pensions

SEDDK internal systems rules, aligned to the ICT Security Guide.

Energy & Critical Infrastructure

EPDK cybersecurity competency model and Law 7545.

Exporters to the EU

KVKK at home; GDPR and the EU AI Act for EU clients.

Spreadsheets and IT-Only Tools Leave agap
Regulators Will Find.

Legacy Enterprise
GRC
Compliance-First Tools
LockThreat
Turkish Frameworks
Custom build
Limited local depth
KVKK, BDDK, SPK, TCMB
GRC Depth
Full G+R+C
Compliance only
Full G+R+C
Deployment
Complex to configure
Typically SaaS only
Private cloud, on-prem, SaaS
Multi-Regulator Mapping
Consultant-heavy
IT controls only
Test once, map across regulators
Continuous Monitoring
Limited or none
IT & cyber only
Enterprise-wide
AI Governance
Separate add-on
Limited
Built-in, incl. agentic AI
Time to Value
12–18 months
Weeks, compliance only
Weeks to months
Turkish Frameworks
Legacy Enterprise GRC
Custom build
Compliance-First Tools
Limited local depth
LockThreat
KVKK, BDDK, SPK, TCMB
GRC Depth
Legacy Enterprise GRC
Full G+R+C
Compliance-First Tools
Compliance only
LockThreat
Full G+R+C
Deployment
Legacy Enterprise GRC
Complex to configure
Compliance-First Tools
Typically SaaS only
LockThreat
Private cloud, on-prem, SaaS
Multi-Regulator Mapping
Legacy Enterprise GRC
Consultant-heavy
Compliance-First Tools
IT controls only
LockThreat
Test once, map across regulators
Continuous Monitoring
Legacy Enterprise GRC
Limited or none
Compliance-First Tools
IT & cyber only
LockThreat
Enterprise-wide
AI Governance
Legacy Enterprise GRC
Separate add-on
Compliance-First Tools
Limited
LockThreat
Built-in, incl. agentic AI
Time to Value
Legacy Enterprise GRC
12–18 months
Compliance-First Tools
Weeks, compliance only
LockThreat
Weeks to months

Frameworks for Türkiye

Mapped to one control library, so a control tested once serves every framework it supports. Tracking something not listed? Ask us.

Categories
No frameworks match your search.

Data Protection

Personal Data Protection Law No. 6698 (KVKK), as amended by Law No. 7499
Regulation on Procedures and Principles for Transfer of Personal Data Abroad (2024)
VERBİS Data Controllers’ Registry
ISO/IEC 27701
GDPR (General Data Protection Regulation)

National Cybersecurity

Cybersecurity Law No. 7545
Presidential Circular No. 2019/12 on Information and Communication Security Measures
Information and Communication Security Guide
NIST CSF 2.0
ISO 22301

Banking & Payments

BDDK Regulation on Information Systems and Electronic Banking Services of Banks
BDDK Regulation on Independent Audit of Information Systems and Business Processes
BDDK Communiqué on Information Systems of Leasing, Factoring and Financing Companies
TCMB Communiqué on Information Systems of Payment and Electronic Money Institutions
PCI DSS
SWIFT Customer Security Programme

Capital Markets, Insurance & Energy

SPK Communiqué on Information Systems Management (VII-128.10)
SPK Communiqué on Independent Audit of Information Systems (III-62.2)
SPK Crypto-Asset Service Provider Communiqués (III-35/B.1, III-35/B.2)
SEDDK Regulation on Internal Systems in Insurance and Private Pensions
EPDK Regulation on the Cybersecurity Competency Model in the Energy Sector

Governance & Risk

SPK Corporate Governance Communiqué (II-17.1)
Turkish Commercial Code, Art. 378: Early Risk Detection Committee
Türkiye Sustainability Reporting Standards (TSRS)
ISO 31000
COSO (Committee of Sponsoring Organizations)

Global Standards & AI

ISO 27001:2022
ISO/IEC 42001 (AI Management System)
NIST AI Risk Management Framework (NIST AI RMF)
EU AI Act
The Risk Nobody’s Governing

Your teams are already using AI on customer and employee data. Under KVKK, you’re accountable for it. Do you know which AI tools and agents are breaching your controls?

AI Security & Governance Flow

Your Data. Your Boundary.

Turkish financial regulators expect core systems to stay in the country: BDDK, TCMB and SPK require primary and secondary systems in Türkiye, and Presidential Circular 2019/12 keeps critical public data at home.

Choose how LockThreat runs: in your own private cloud, on-premises in your Turkish data centre, or as managed SaaS. The same full G+R+C depth, regardless of deployment.

SaaS
Managed by us.
Private Cloud
Your cloud. Your region.
On-Premises
Fully within your walls.

One Platform for the Whole Buying Committee

Blue shield icon with a white award ribbon symbol featuring a star in the center.Vertical flowchart with four outlined circles connected by dotted lines in dark blue, beige, and light blue colors.
CISO
  • BDDK, SPK and Cybersecurity Law evidence collected continuously, not the week before an audit.
  • Third-party and outsourcing risk tracked alongside your own controls.
Line drawing of a human head and upper torso facing forward with a large dark blue dot near the brain area and a smaller bright blue dot near the upper chest.
DPO & Chief Compliance Officer
  • KVKK obligations mapped to controls, with the 72-hour breach clock tracked in incident workflows.
  • Transfer safeguards and policies documented against the frameworks you answer to.
Line art icon with a stylized head and shoulders and three floating dots above representing communication or connection.
CRO & Early Risk Detection Committee
  • Risk quantified in financial terms with FAIR modelling and Monte Carlo simulation.
  • One enterprise risk register across business units and locations.
Two overlapping blue circles connected by a black diagonal line on a white background.
Internal Audit & Audit Committee
  • Continuous control testing instead of periodic sampling.
  • Board and committee reporting drawn from live data, not spreadsheets.
Outline of a person’s head and shoulders with a blue circle above representing the mind or focus.

Everything Enterprise GRC Should Have Been.

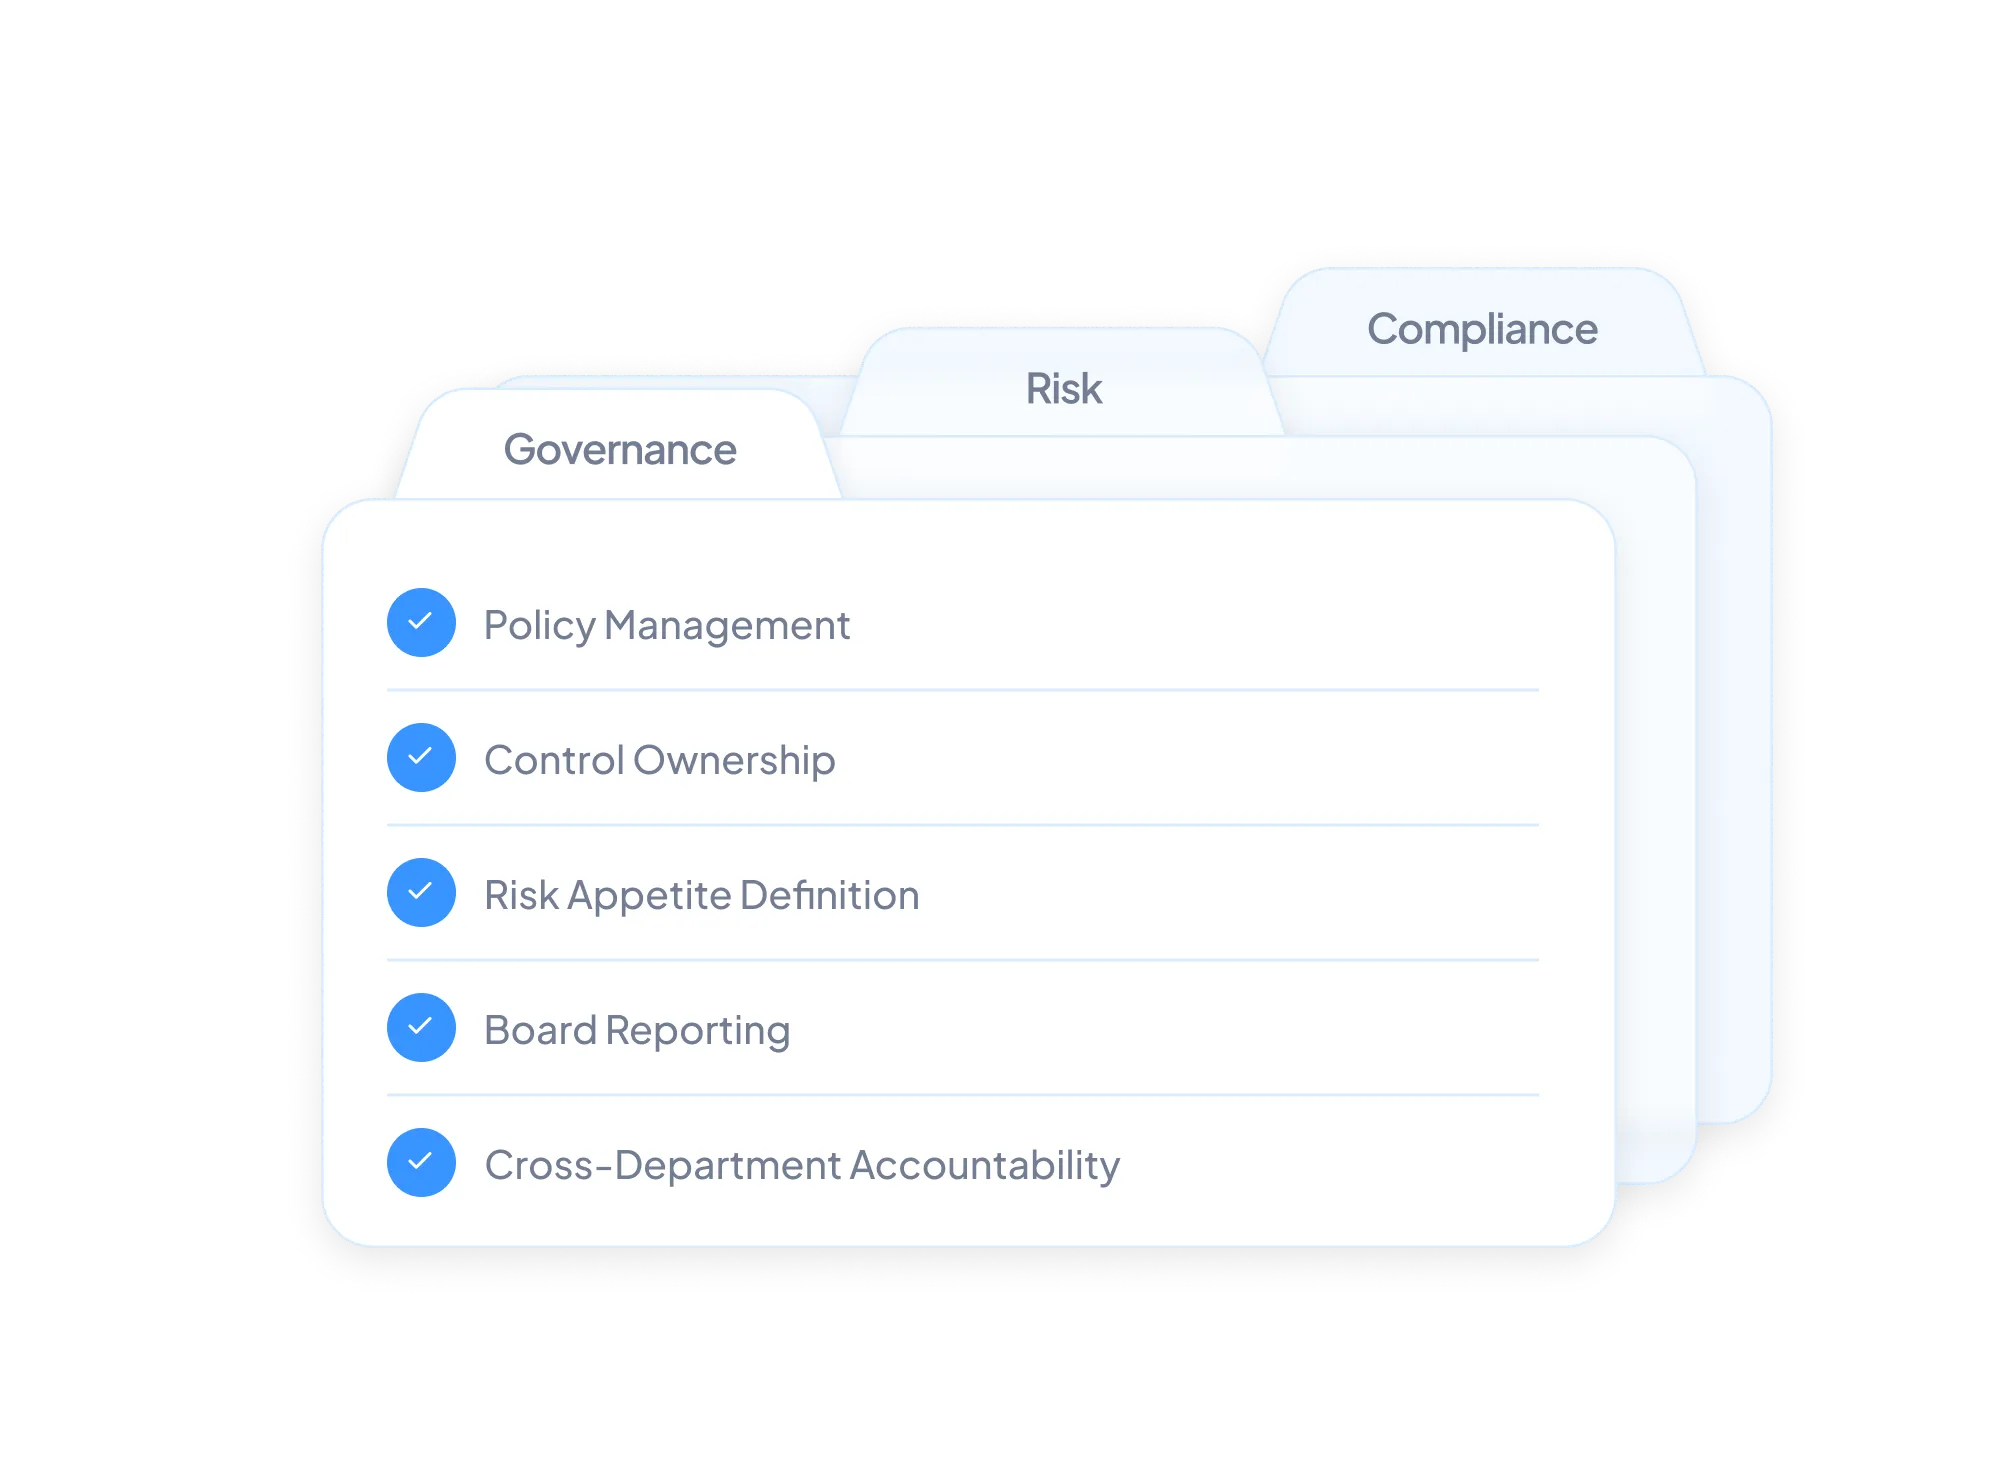
True GRC Depth

Most GRC tools deliver compliance, with governance and risk as an afterthought.

Here, governance comes first: the policies that move your organisation forward, the controls that contain risk across every department, and the compliance that follows naturally from both.

No spreadsheets. No disconnected tools. No point-in-time snapshots. One centralised, ongoing view of your risk and compliance posture.
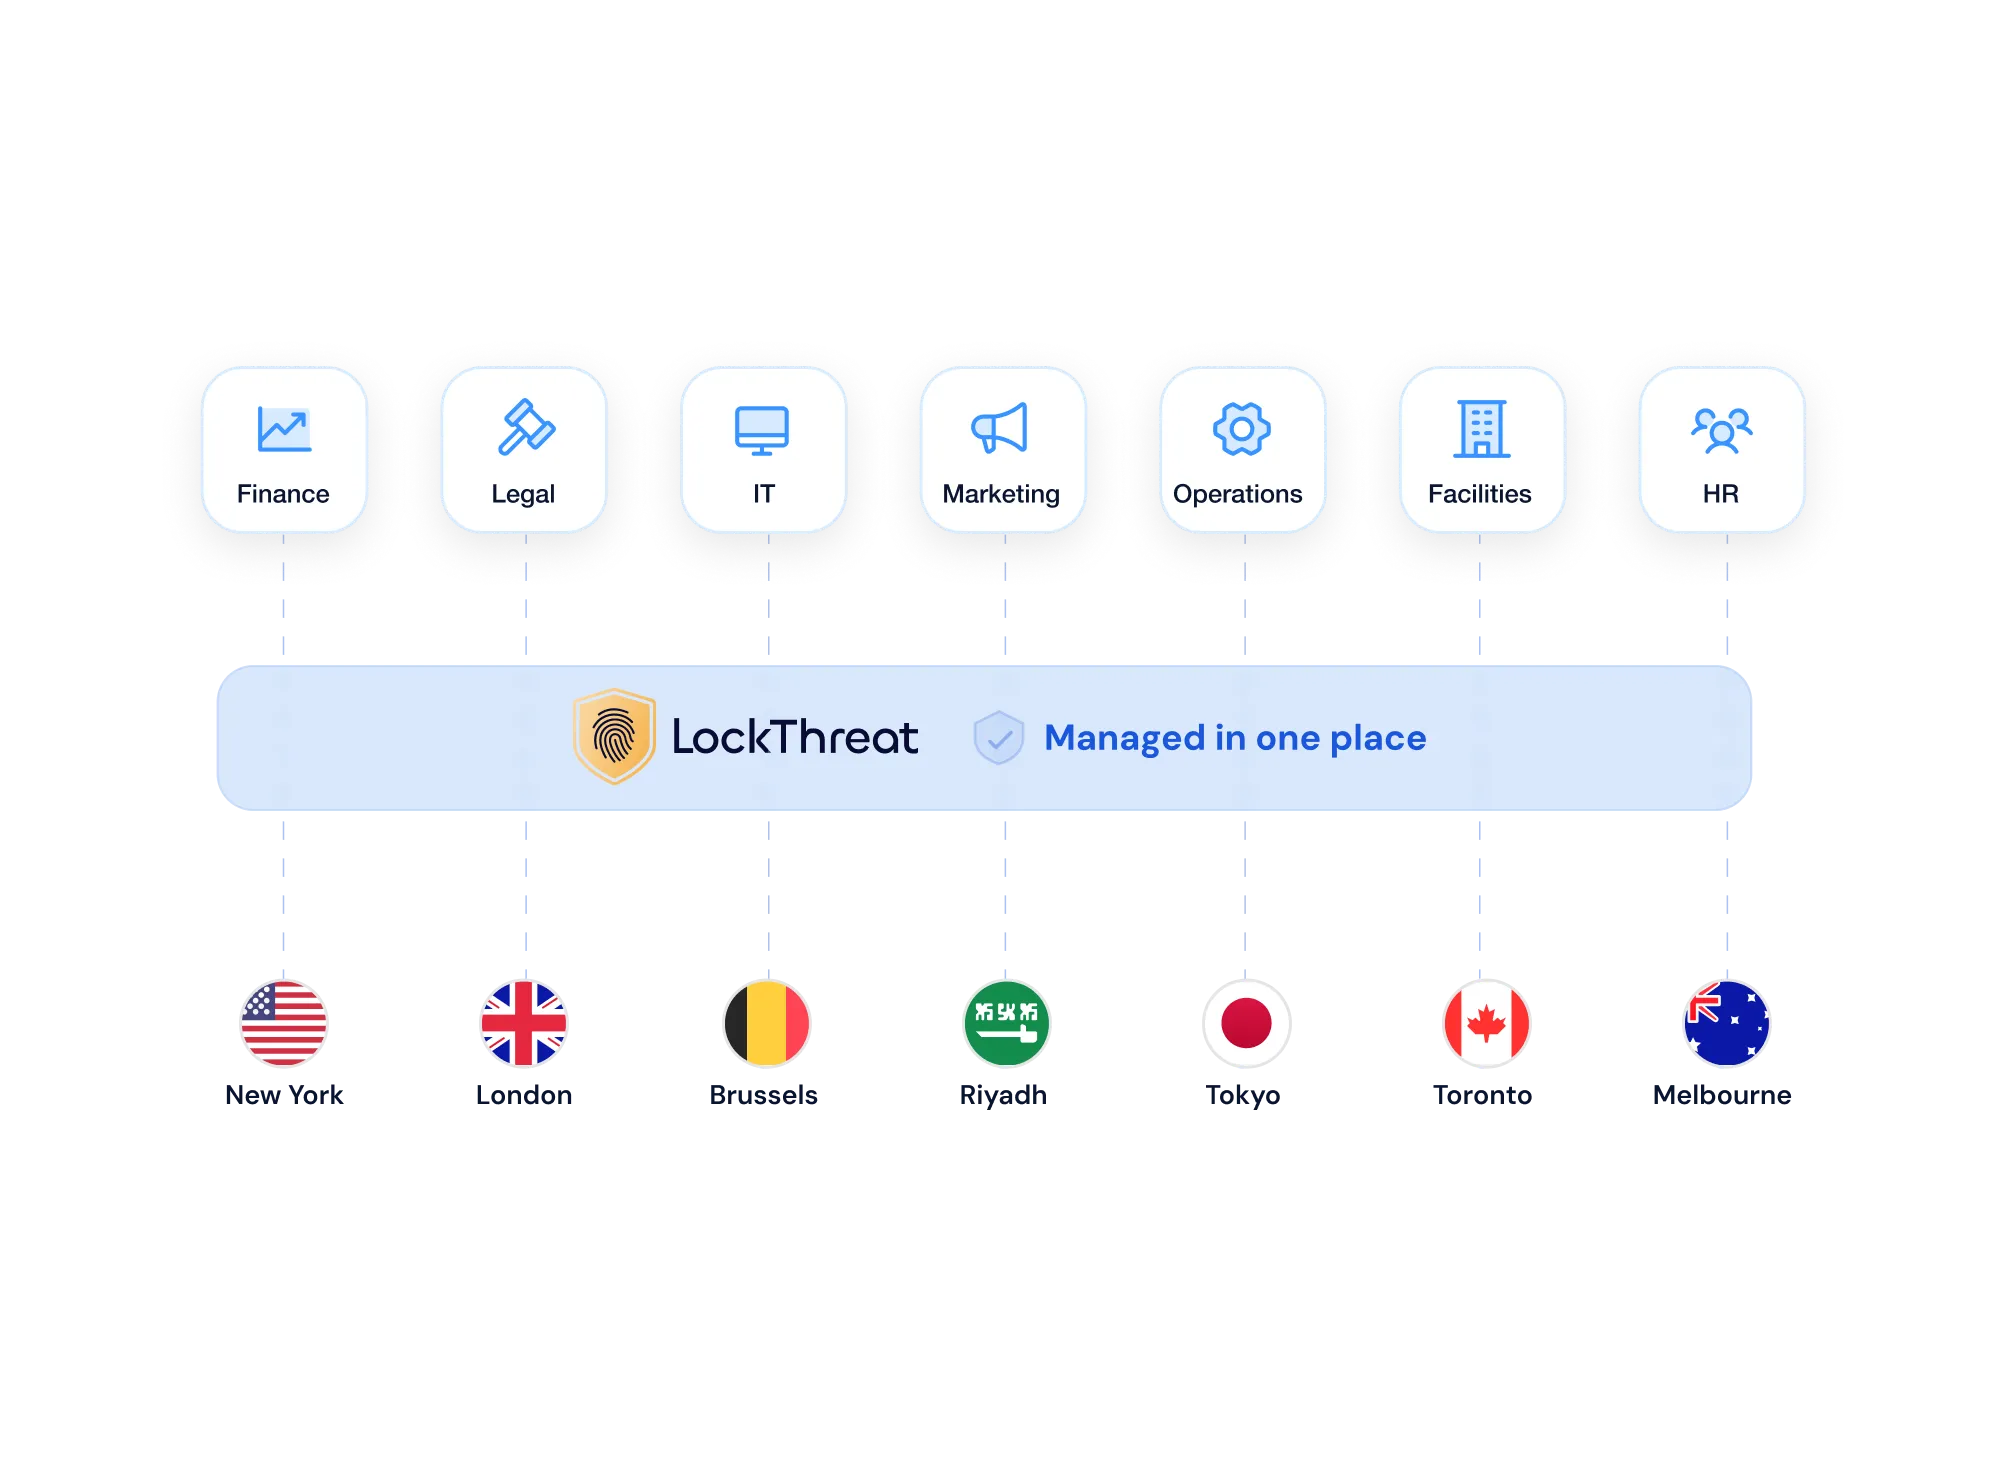
GRC for Everyone

Your regulatory obligations don’t respect org charts or borders.

Every department, from finance, legal and HR to operations, cyber and IT, managed in one place, without the sprawl.

The locations you operate in, from Istanbul, Ankara and İzmir to your plants, branches and offices worldwide, managed in one place without adding more tools.
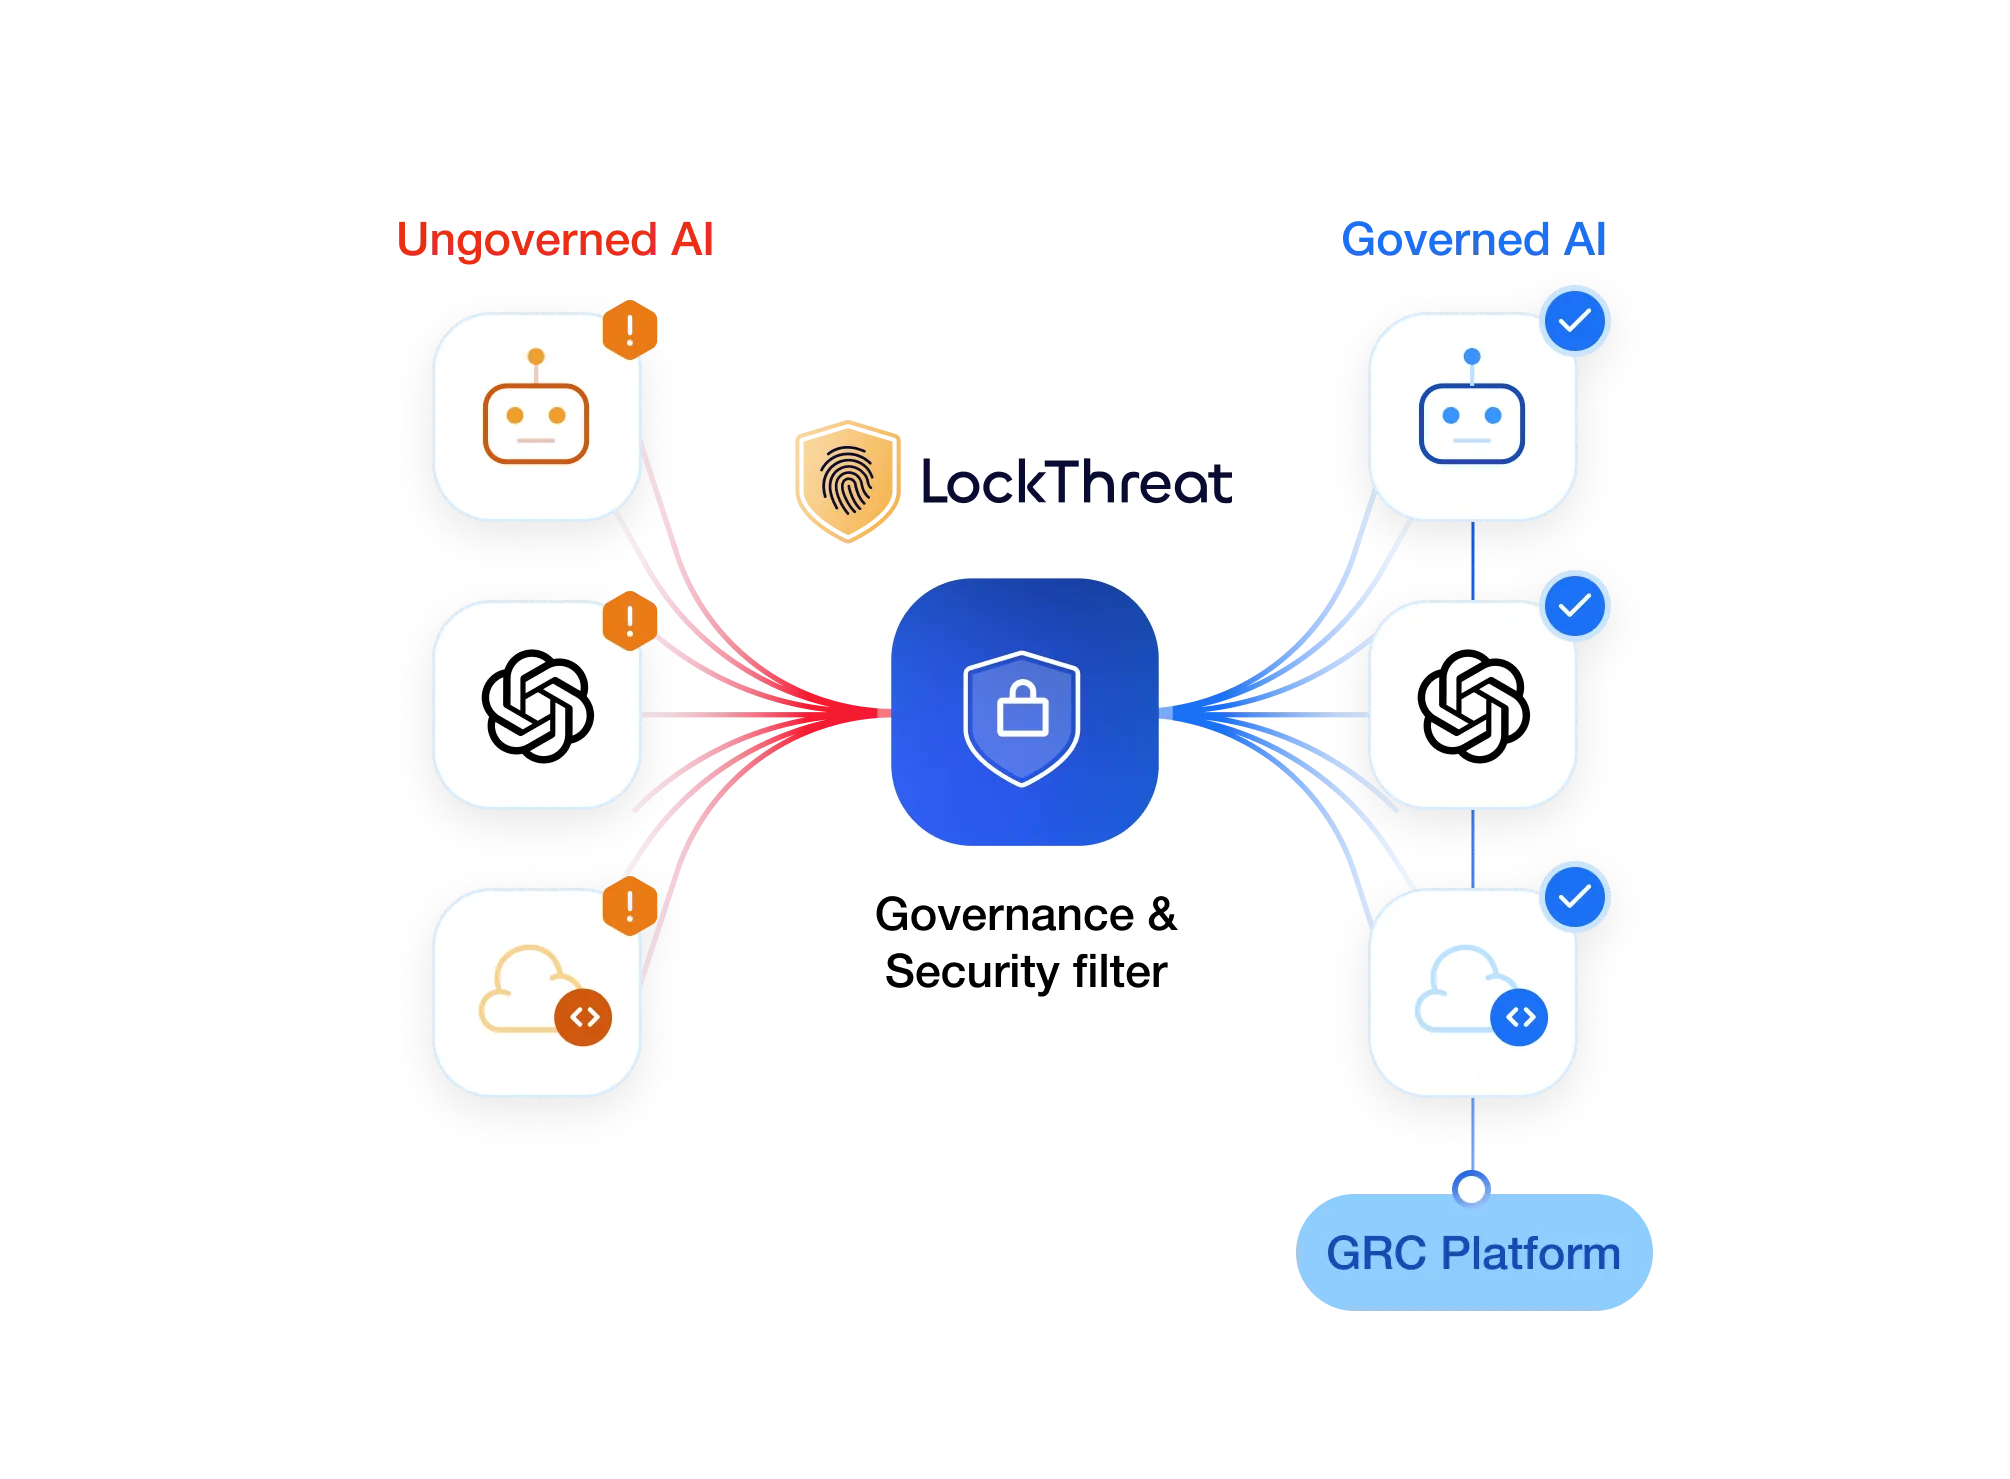
AI Governance & Security

Which AI tools are your employees using? Are they approved? Are they handling personal data your KVKK notices and consents don’t cover?

And when AI agents act autonomously, accessing systems, making decisions, breaching controls, who’s watching? Now you are.

From shadow AI discovery and ISO/IEC 42001 alignment to real-time prompt protection and agentic control enforcement, reported directly into your GRC framework.
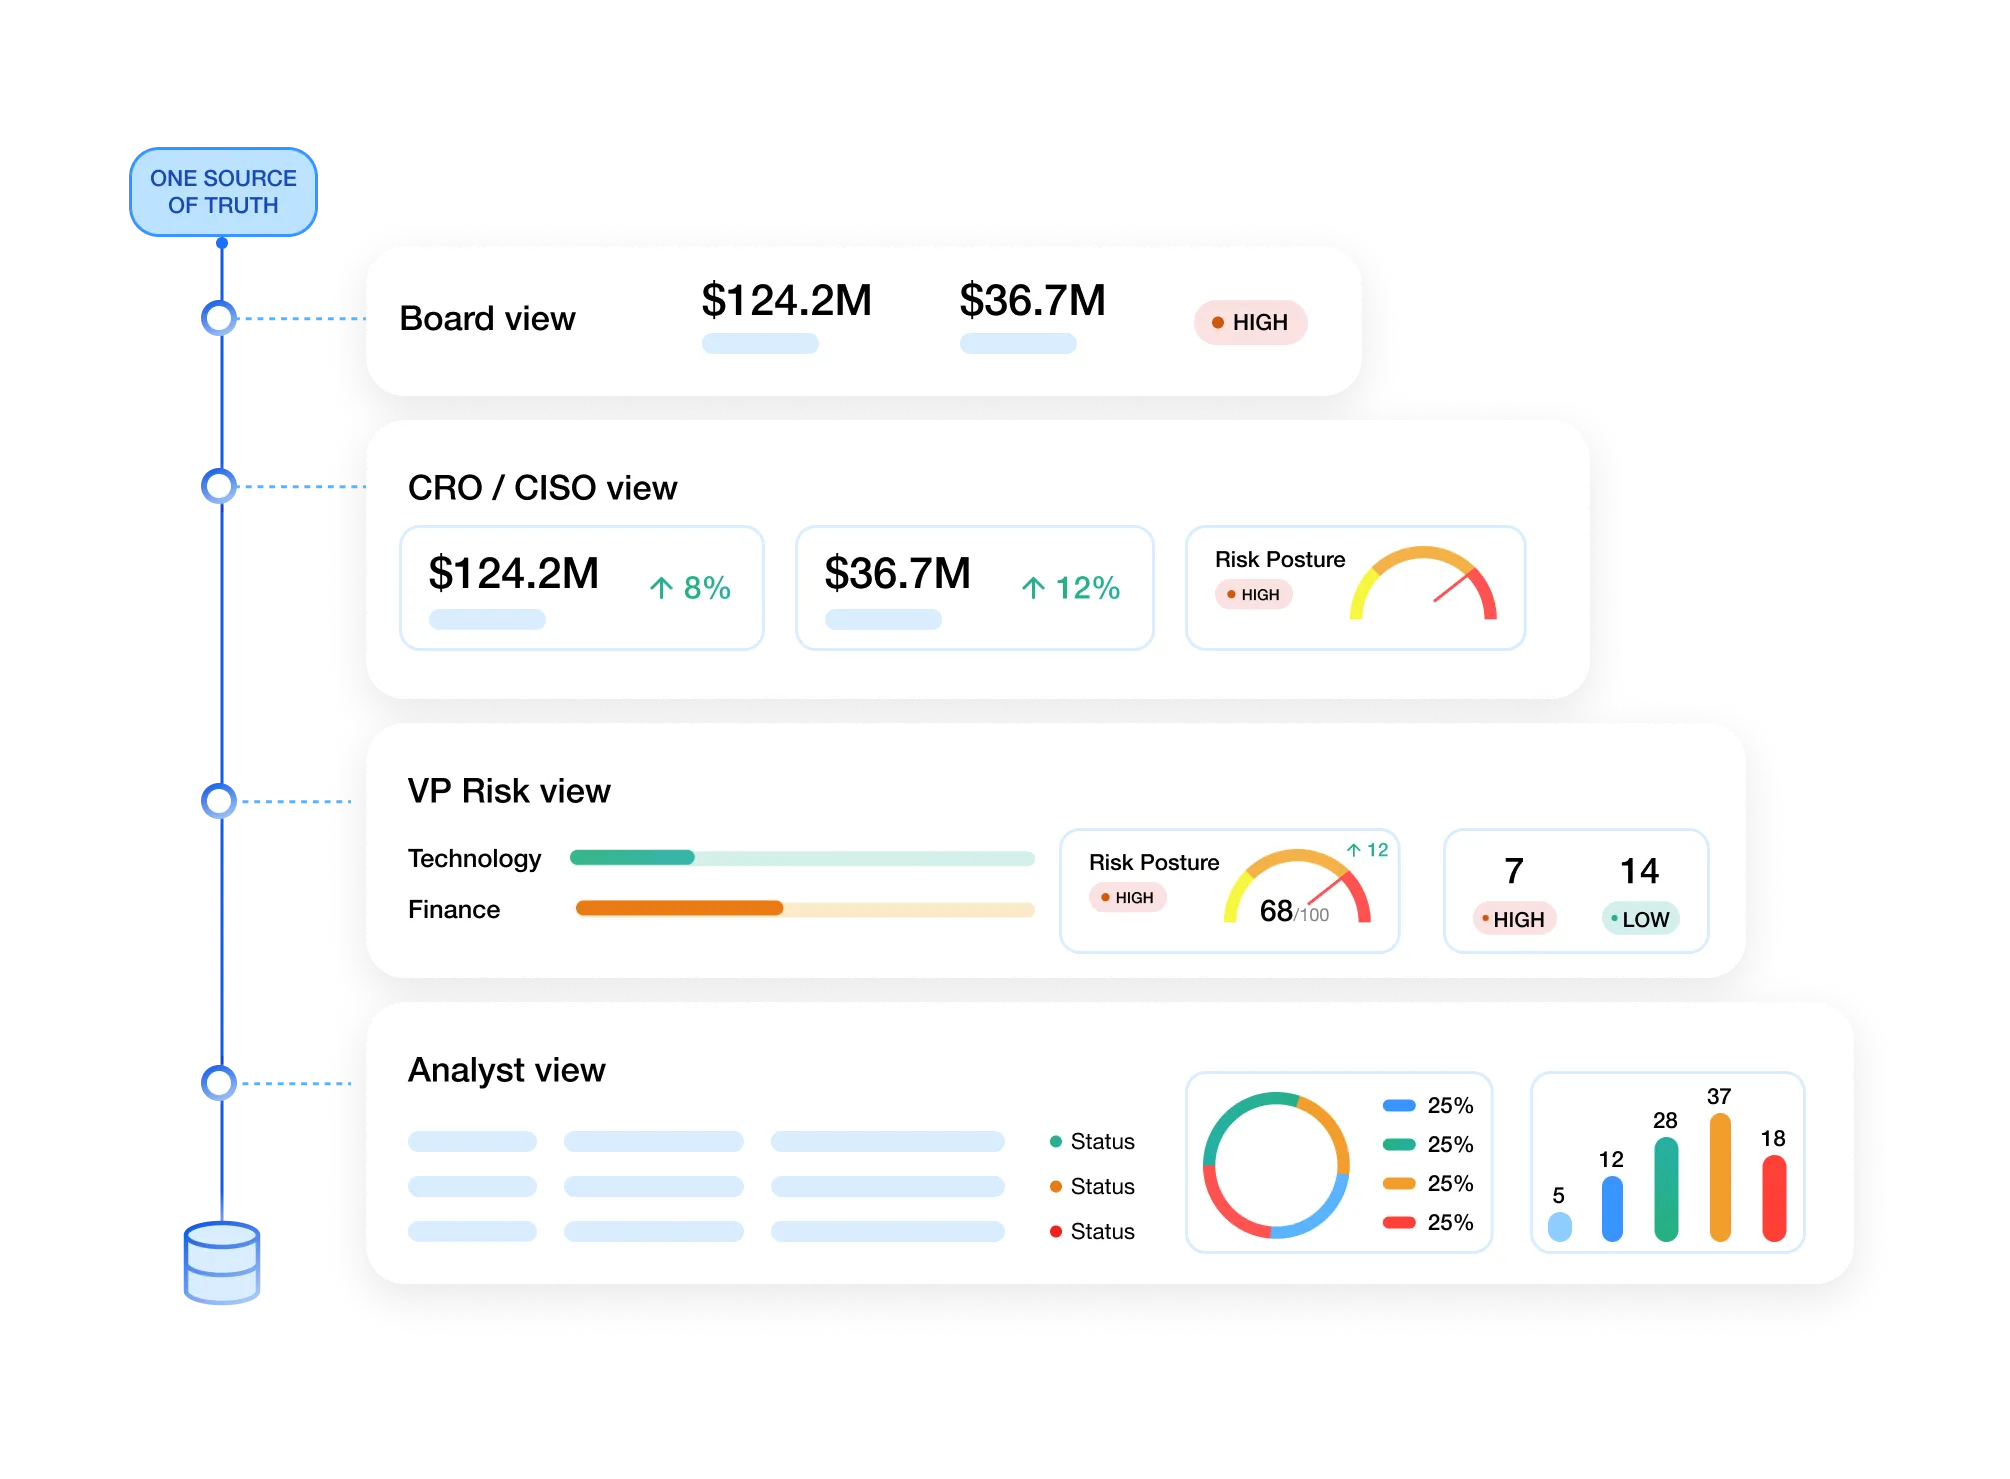
Risk Clarity

Every stakeholder needs a different view of the same risk reality, from one source of truth.

Express risk in financial terms your board and CFO can act on, using FAIR modelling and Monte Carlo simulation.

Detailed enough for the analyst, clear enough for the Chief Risk Officer and the CISO, compelling enough for the board.
Continuous Assurance

Compliance isn’t an annual exercise; it’s an ongoing operating requirement.

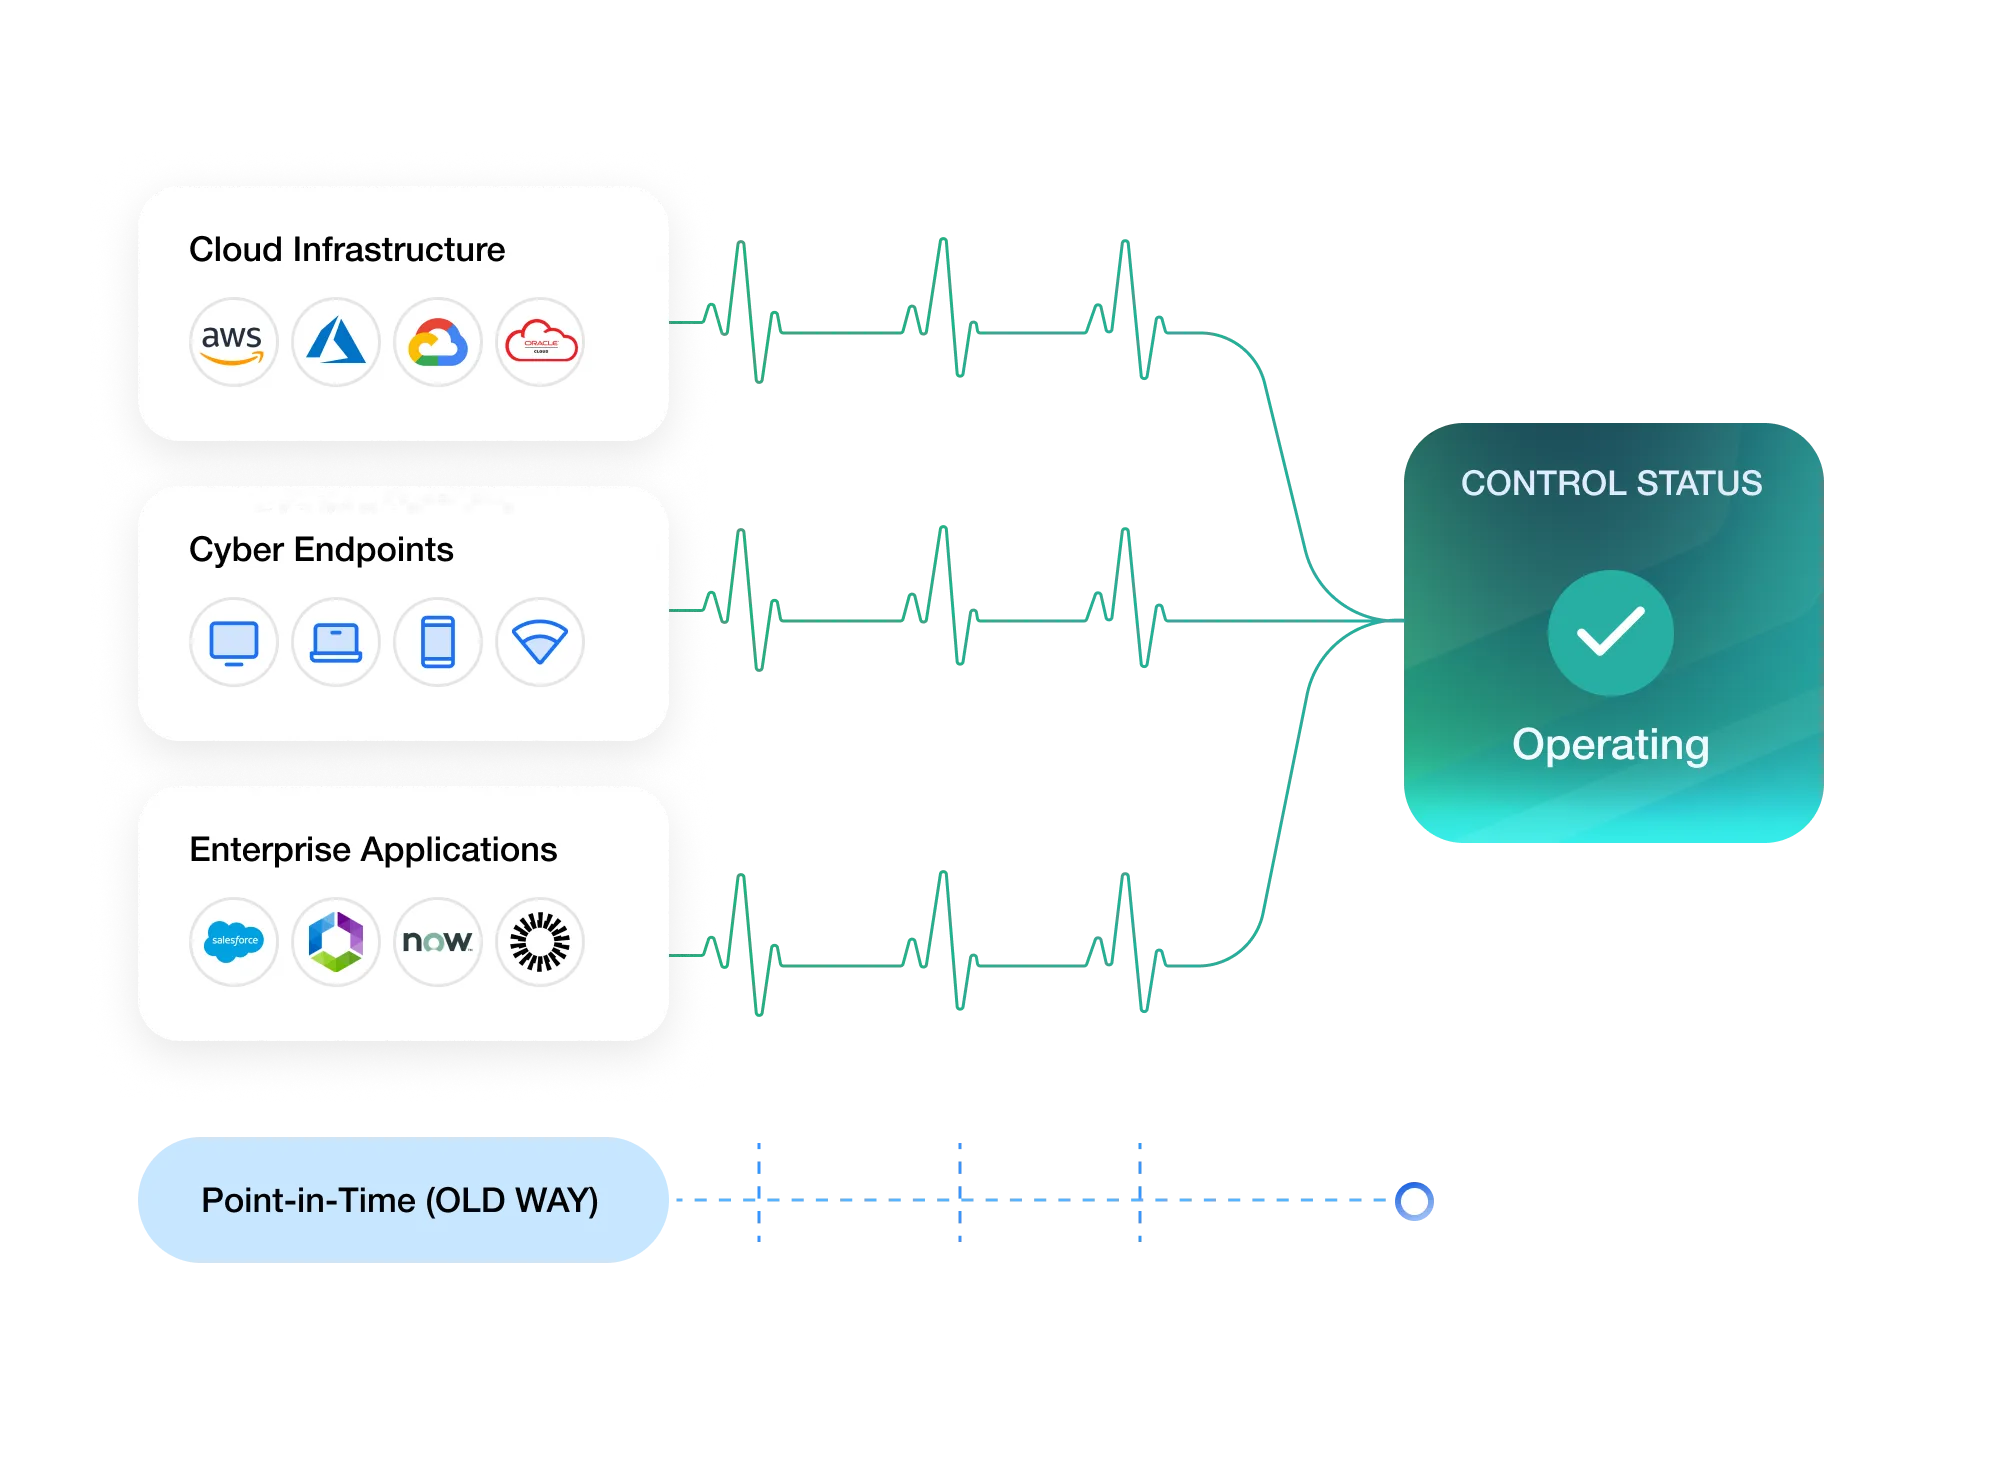
LockThreat validates that your controls are working, right now, across cloud infrastructure, cyber endpoints and enterprise applications.

Far less scrambling for evidence before a BDDK inspection, an independent IS audit or a KVKK review.
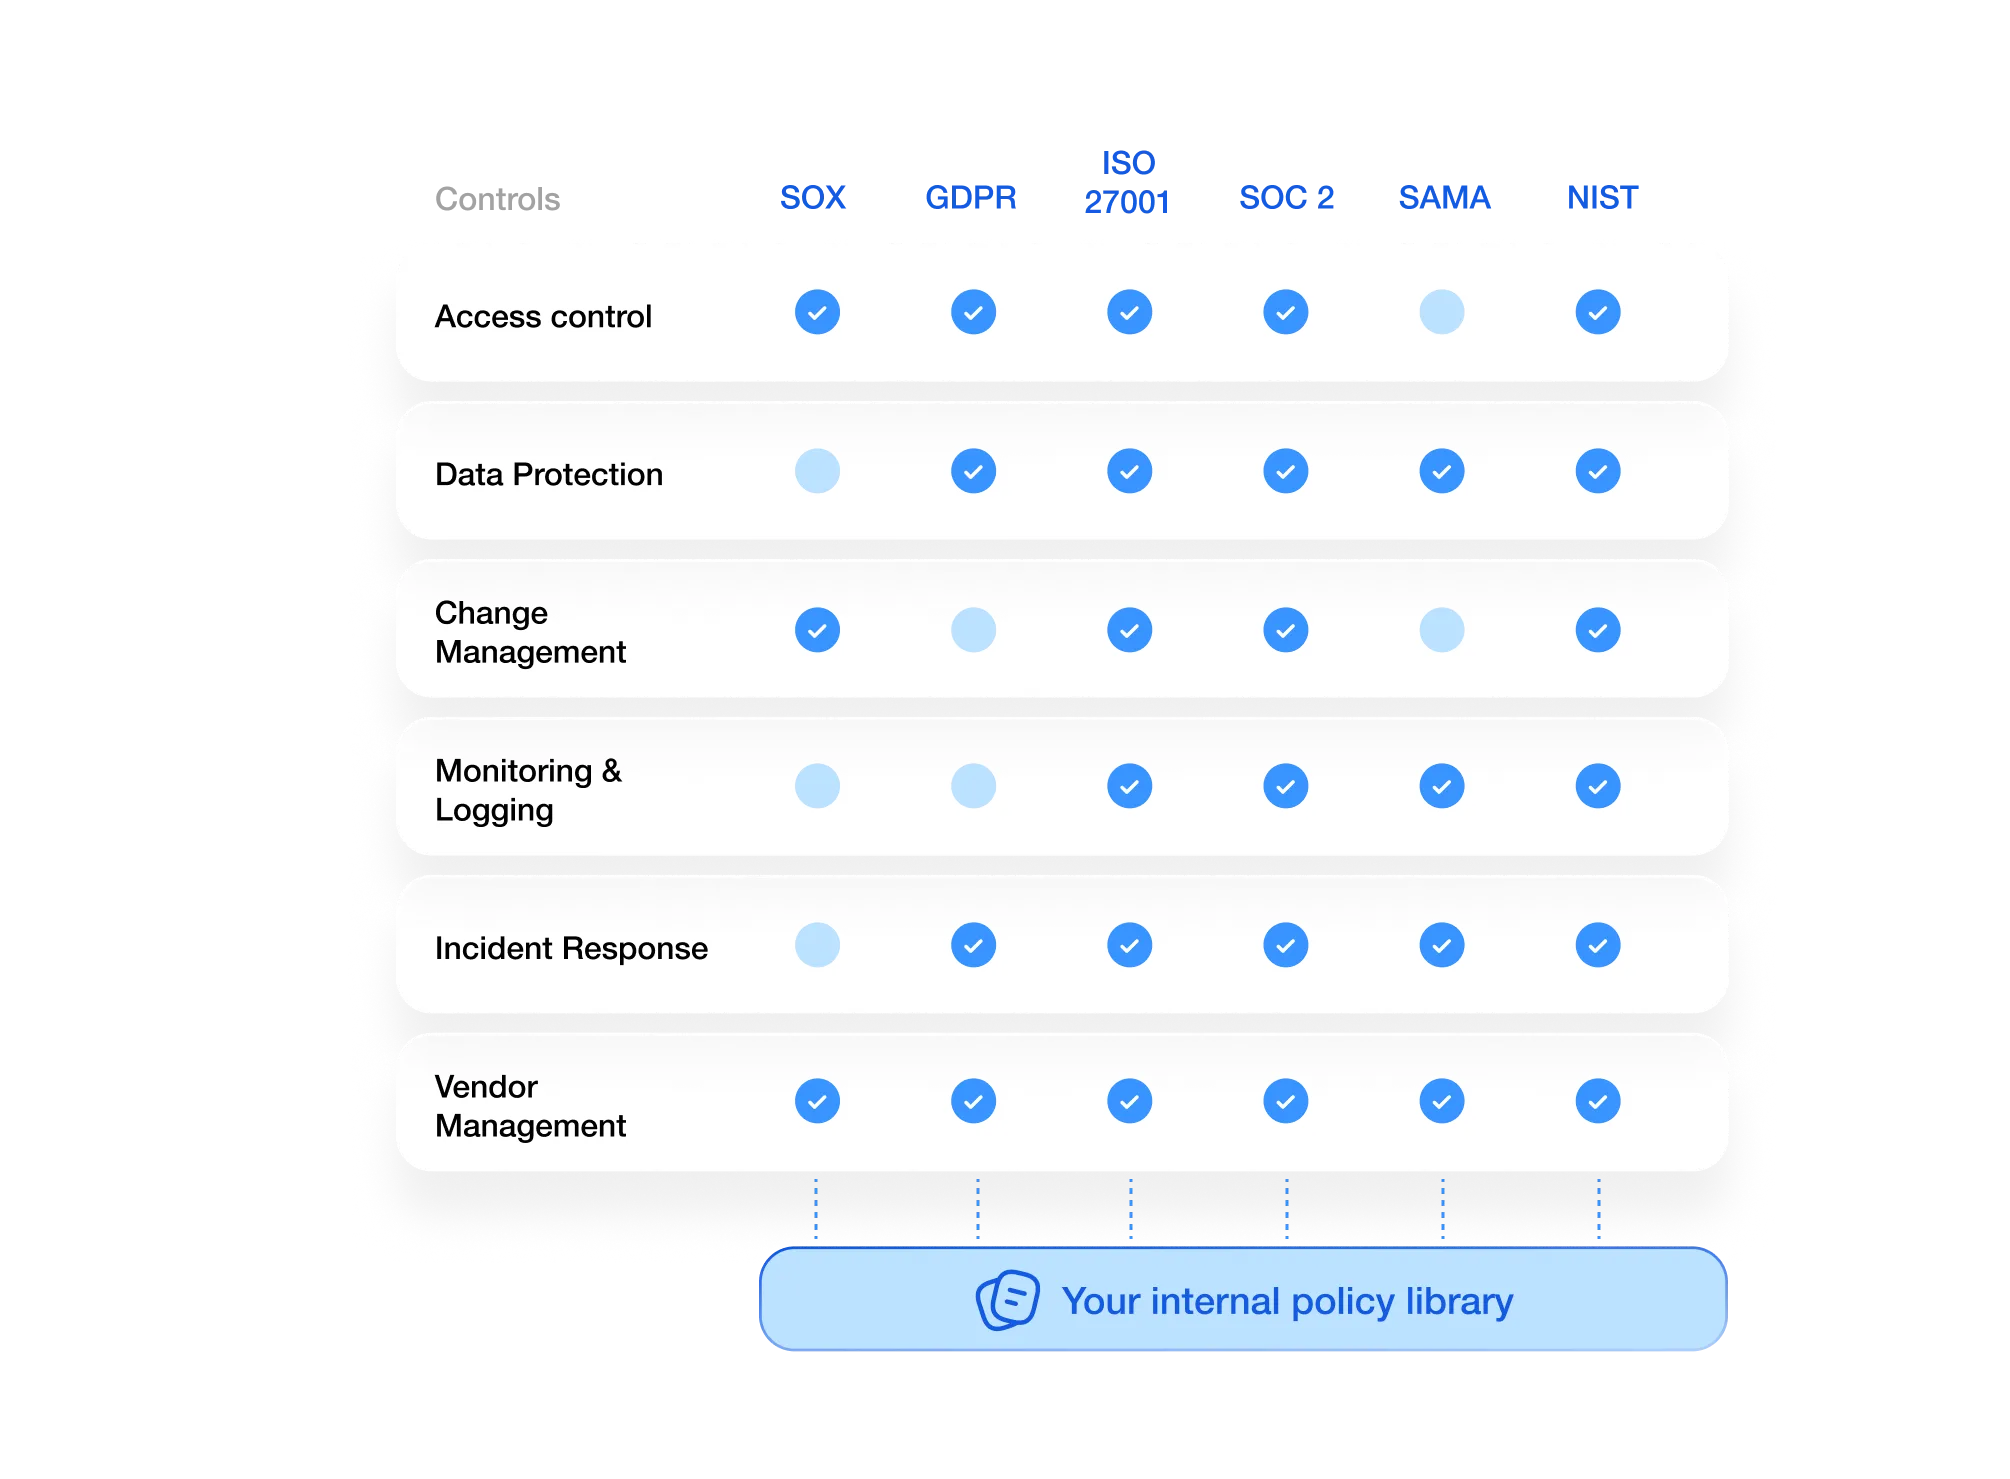
Framework Convergence

Map KVKK, BDDK, SPK and TCMB requirements, Law 7545 and the ICT Security Guide to ISO 27001, NIST and SOC 2, and to each other, eliminating redundant work.

Tie everything to your own policy library and control framework, so governance becomes a living system, not a compliance filing cabinet.
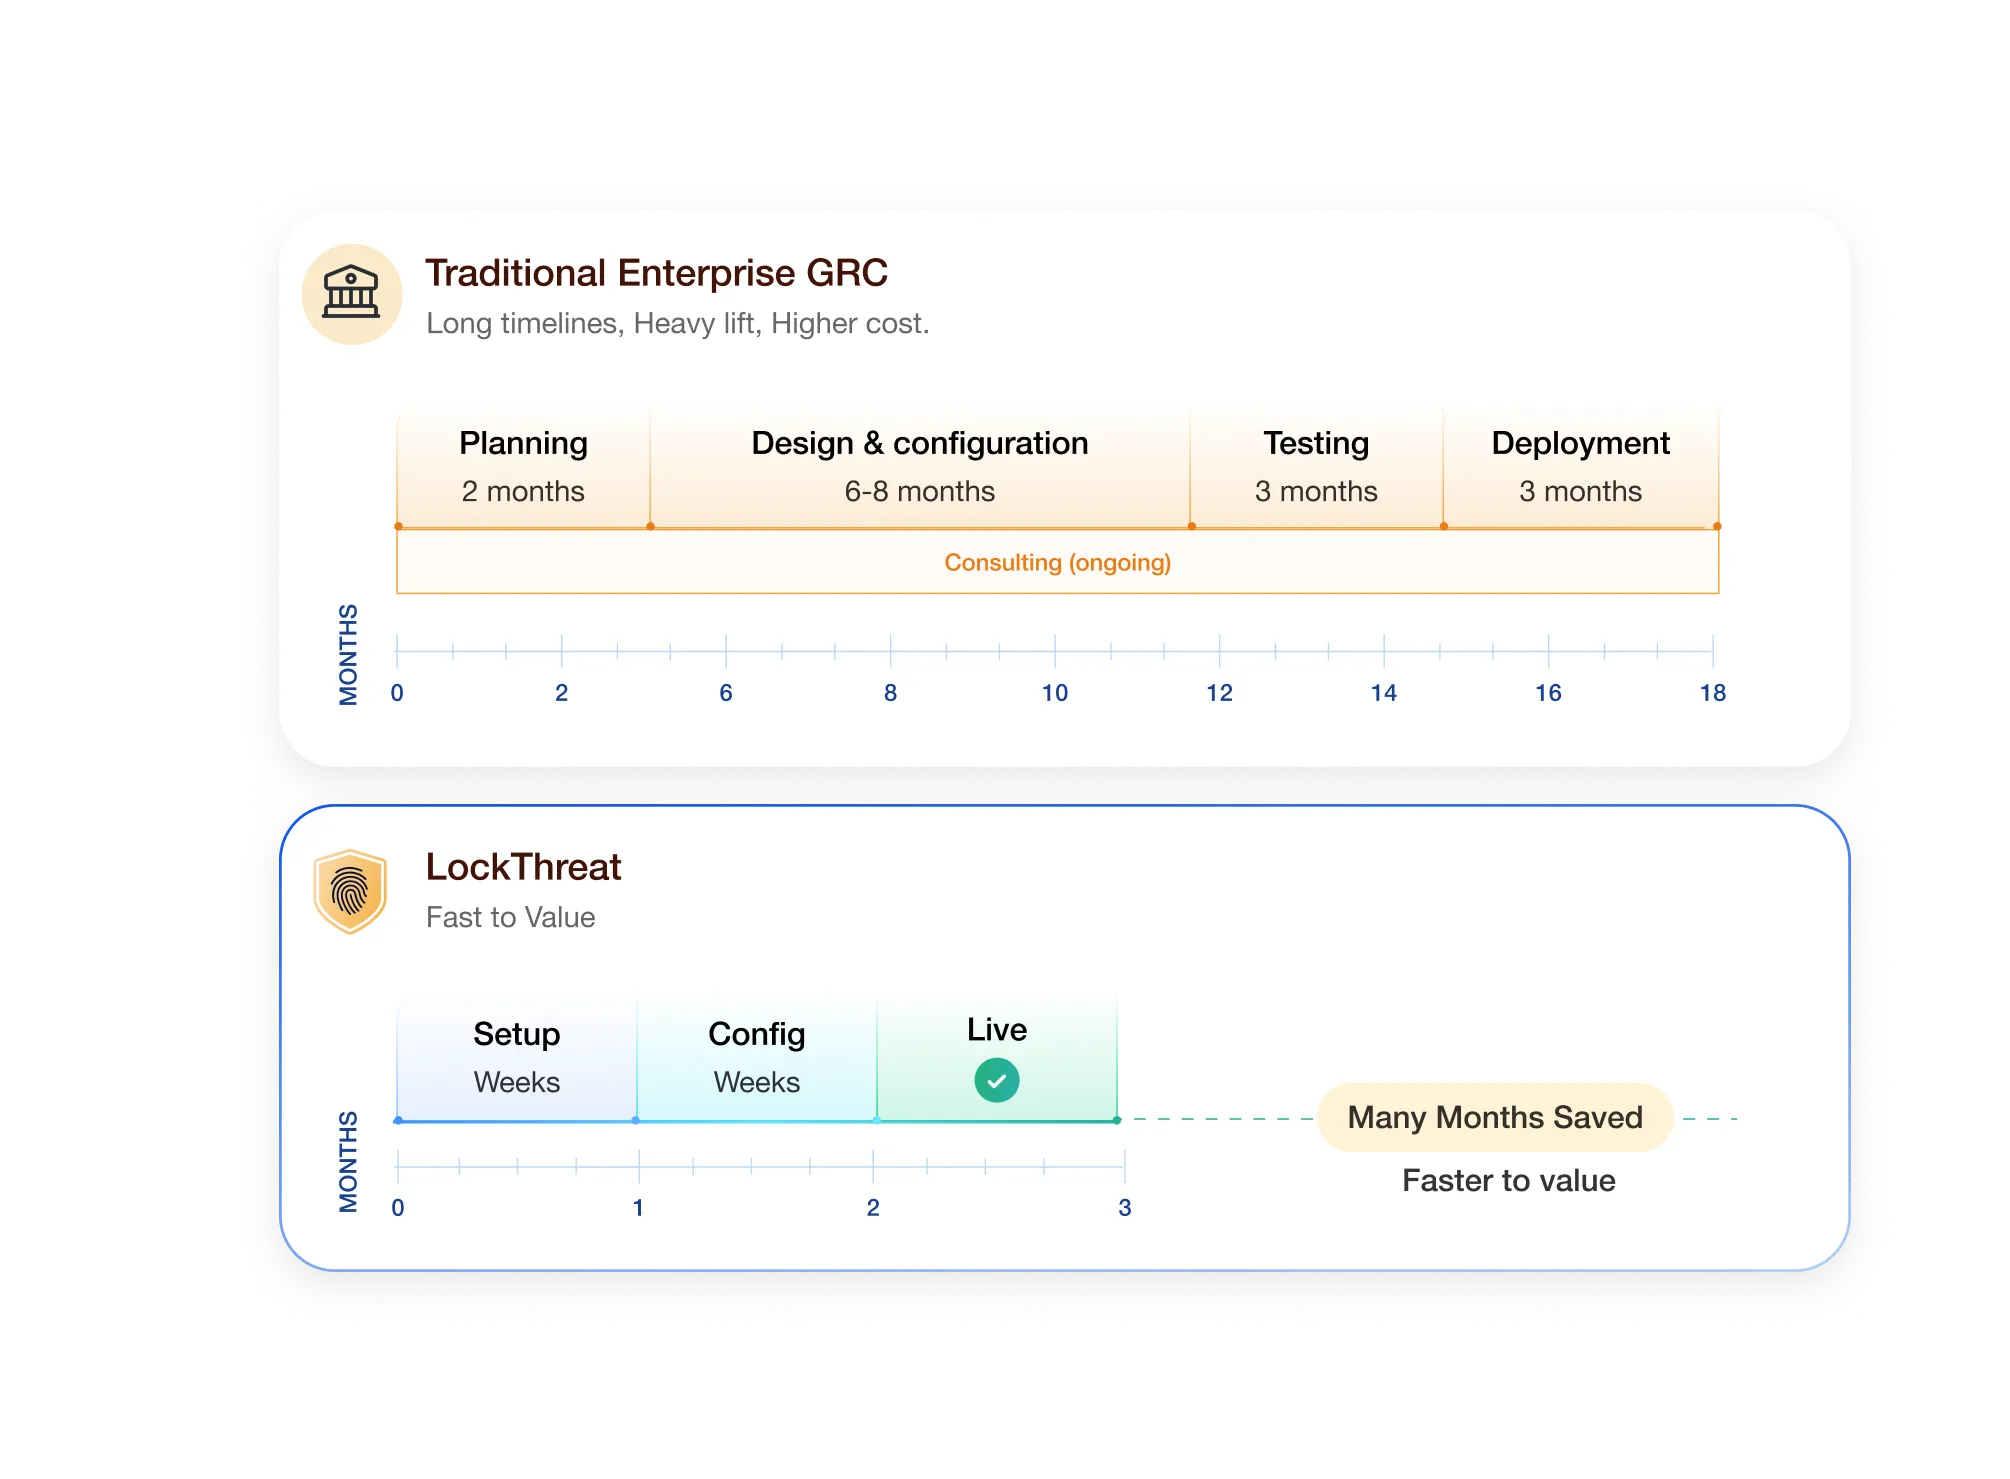
Fast Time to Value

Enterprise GRC depth without the 18-month implementation. Up and running in weeks to months, on the technology stack you already have.

Minimal dependence on scarce specialists once you’re live.

Already running another GRC platform? Run LockThreat alongside it during transition, no rip-and-replace required.
What GRC Leaders Say

Compliance across multiple international standards used to be a serious resource drain. LockThreat unified everything into one platform and eliminated the spreadsheet chaos entirely. It’s been a game-changer for our team.

Director of Risk & Compliance
World’s Most Sustainable City

LockThreat gave our team a single pane of glass across every framework we manage. What used to take weeks of manual mapping now happens automatically. Our clients see faster results and our consultants can focus on higher-value work.

Managing Director
Big-4 Professional Services Firm

We evaluated a lot of GRC tools and nothing came close to LockThreat’s combination of breadth across governance, risk and compliance, combined with AI automation and ease of use. Our team was up and running quickly, and the cross-framework mapping alone saved us hundreds of hours.

VP of Security & Risk
CirrusLabs

The real-time evidence validation and risk dashboards gave our leadership team the visibility they needed without burdening our security team. LockThreat just works.

Head of GRC
Octave

LockThreat fits perfectly into an agile environment. Controls and policies evolve alongside our work. It’s not a static compliance checkbox, it’s a living system that keeps up with our pace.

VP of Security
Agile Trailblazers

Connects to Your Existing Stack

See LockThreat on Your Turkish Frameworks

A focused 30-minute walkthrough, plus pricing for your deployment. No generic pitch, no obligation.

Tell us which regulators and frameworks you answer to (KVKK, BDDK, SPK, TCMB or Law 7545) and how you want to deploy. We’ll tailor the session to your programme.

  1. A 30-minute walkthrough on your frameworks, following your priorities.
  2. Your deployment path: private cloud, on-premises in your data centre, or SaaS.
  3. Pricing for your scope, based on your entities, frameworks and deployment model.

Prefer email? info@lockthreat.com